Cloud security
31 posts, newest first.
#agentless-scanning#alert-management#alerts#attack-paths#automation#azure-devops#azure-event-grid#azure-firewall#azure-key-vault#azure-logic-apps#azure-storage#azure-subscriptions#azure-virtual-machines#cloud-security#cloud-security-graph#cloudflare#code-scanning#codeql#configuration#container-security#credential-security#cspm#cybersecurity#data-protection#defender-for-cloud#defender-for-servers#defender-for-storage#delegated-bypass#dependabot#devops-security#devsecops#dns#firewall-policy#github#github-actions#github-advanced-security#github-code-security#github-secret-protection#governance#governance-rules#infrastructure-as-code#linux#log-analytics#malware-scanning#msdo#network-security-groups#performance#permissions#pull-request-annotations#push-protection#regulatory-compliance#remediation#rule-configuration#secret-scanning#secure-score#security-architecture#security-benchmark#security-configurations#security-posture#security-prioritisation#security-workflow#structured-logging#supply-chain-security#suppression-rules#troubleshooting#vm-security#vulnerability-management#waf#workload-protection#zero-trust
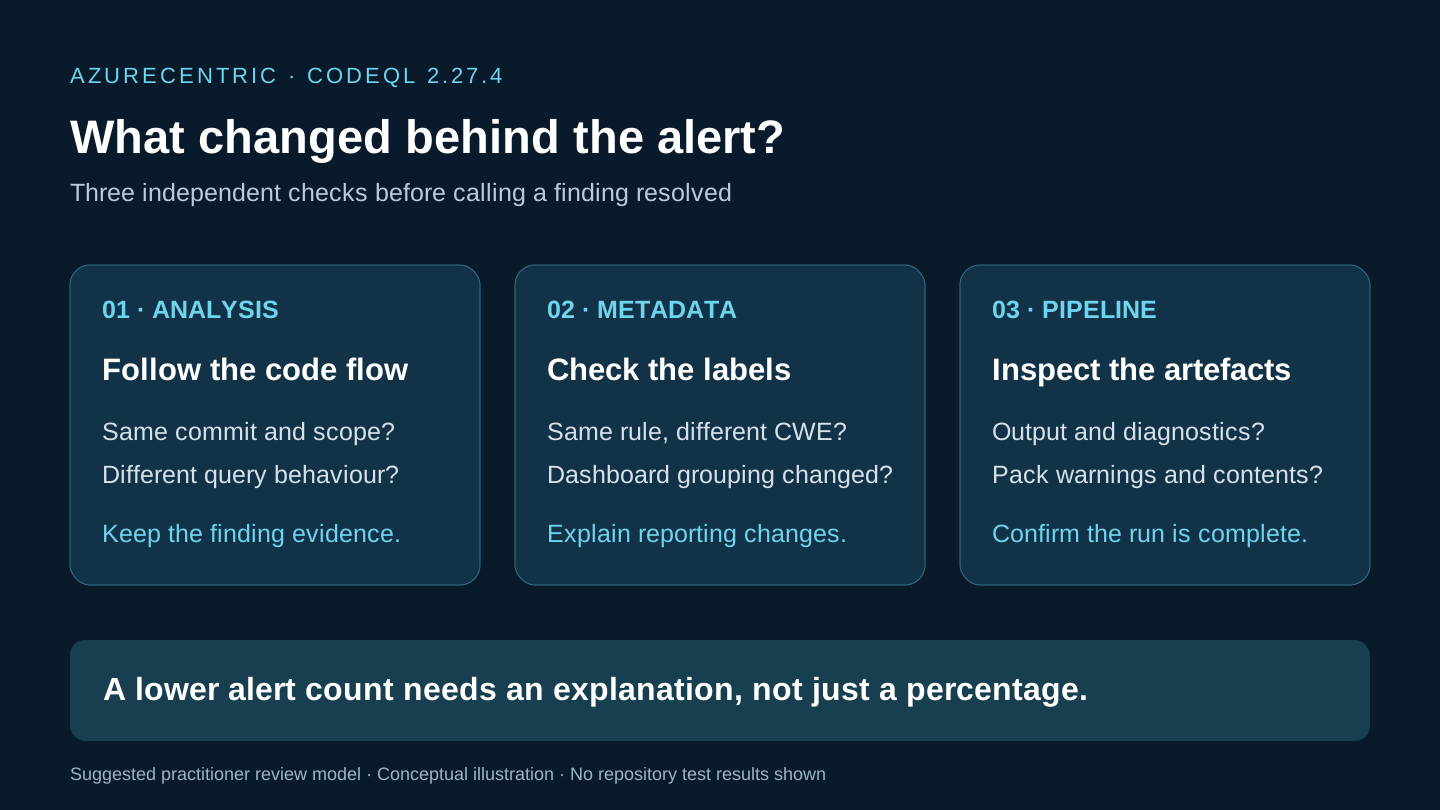 CodeQL 2.27.4: what to check before closing alerts Review the CodeQL 2.27.4 announcement through query changes, CWE reporting and pipeline checks before interpreting a smaller alert backlog.
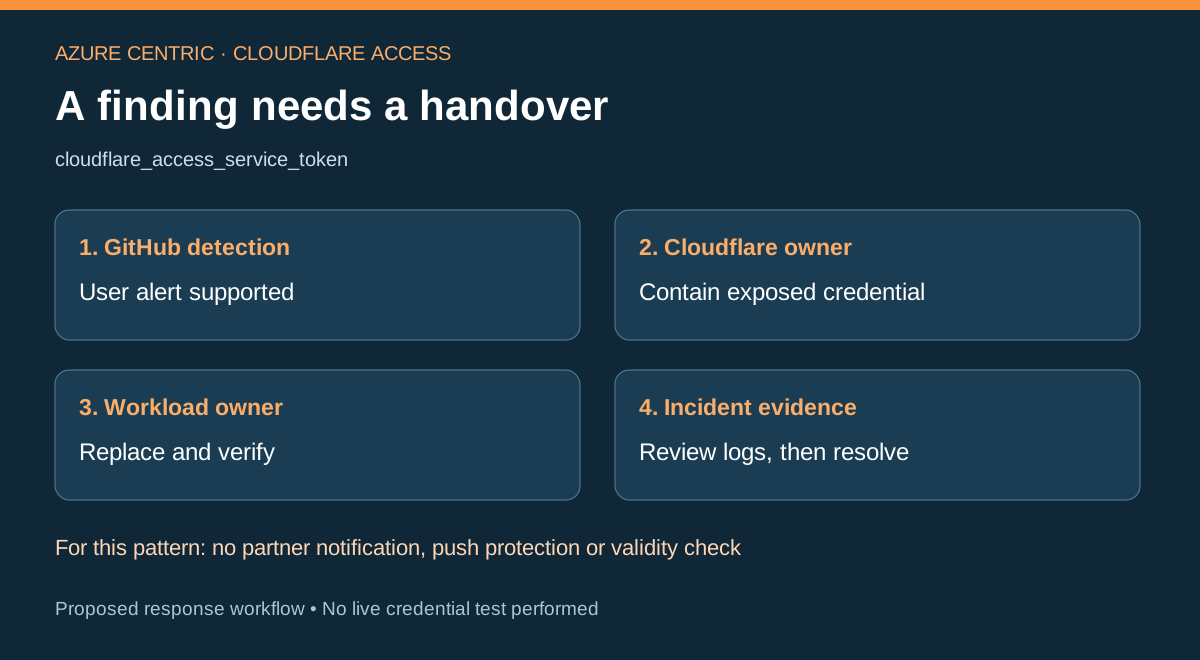 Cloudflare service-token detection: keep revocation in the runbook
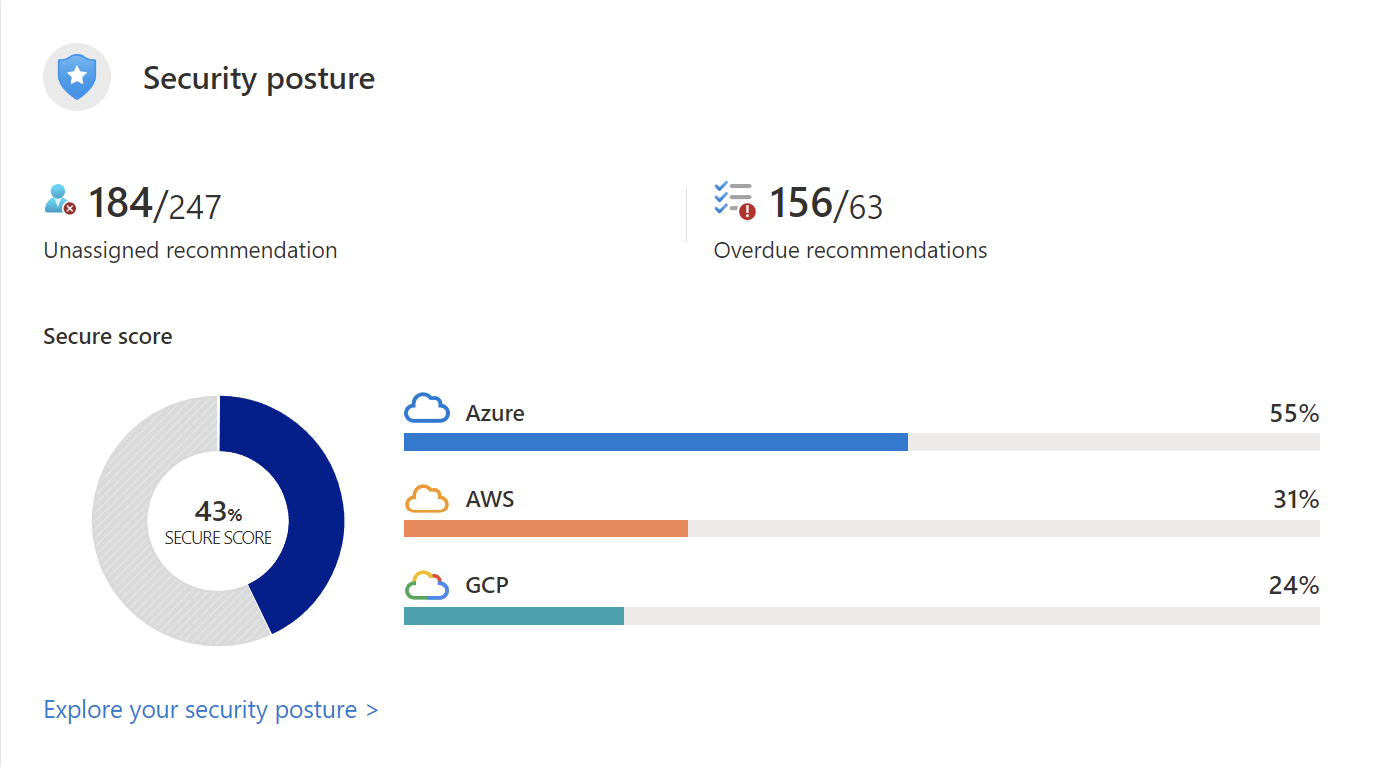 Secure score that drives action, not a weekly percentage
All posts in this category
 Dependabot’s inactivity pause: check coverage before 8 December
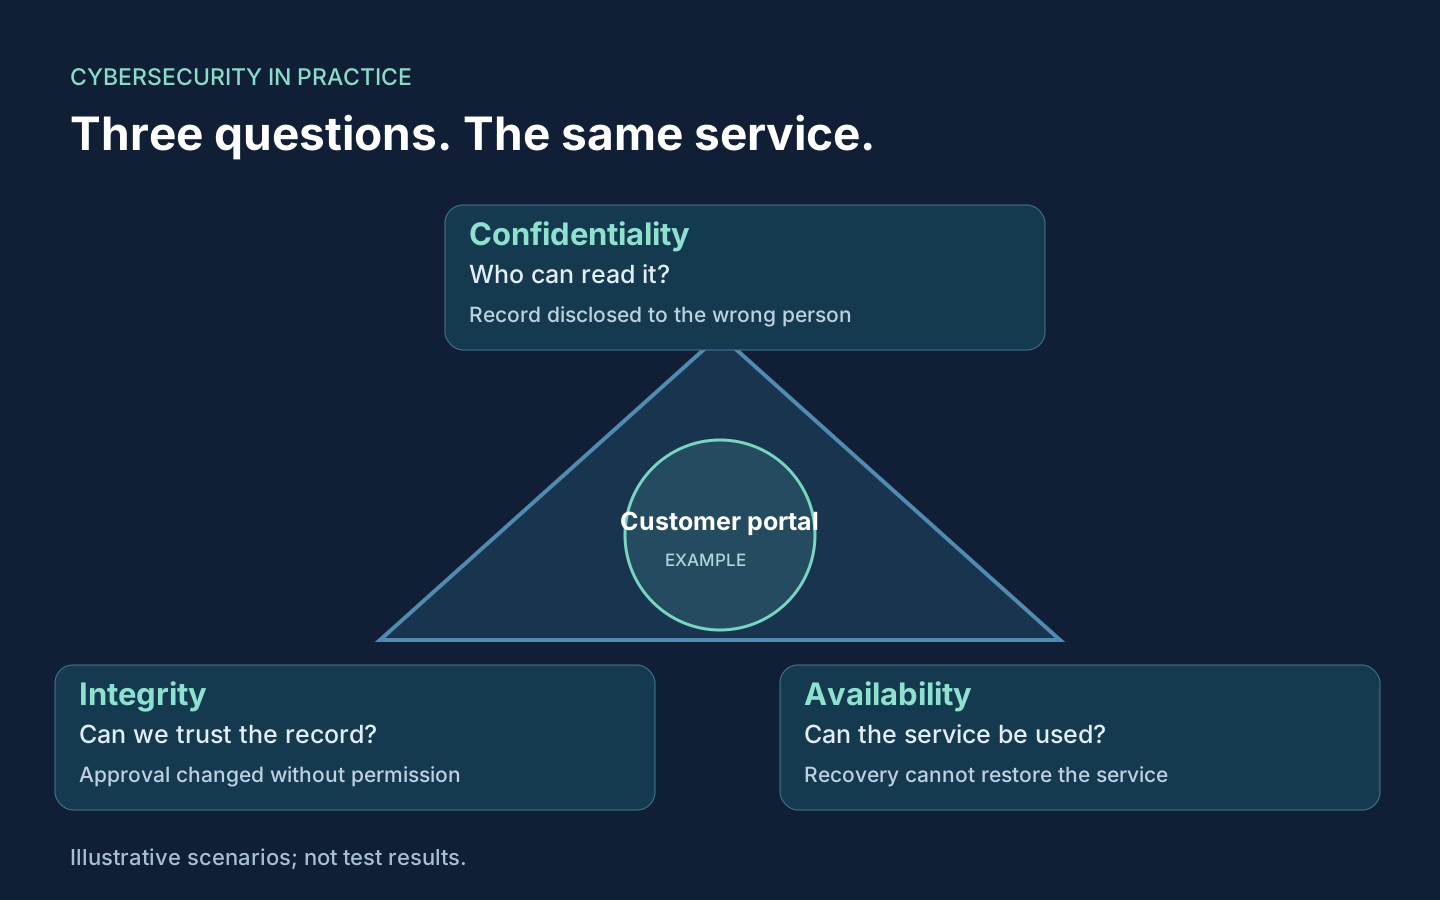 The CIA triad: three questions to ask about the same service
 GitHub secret scanning: review the new filters and your rotation runbook
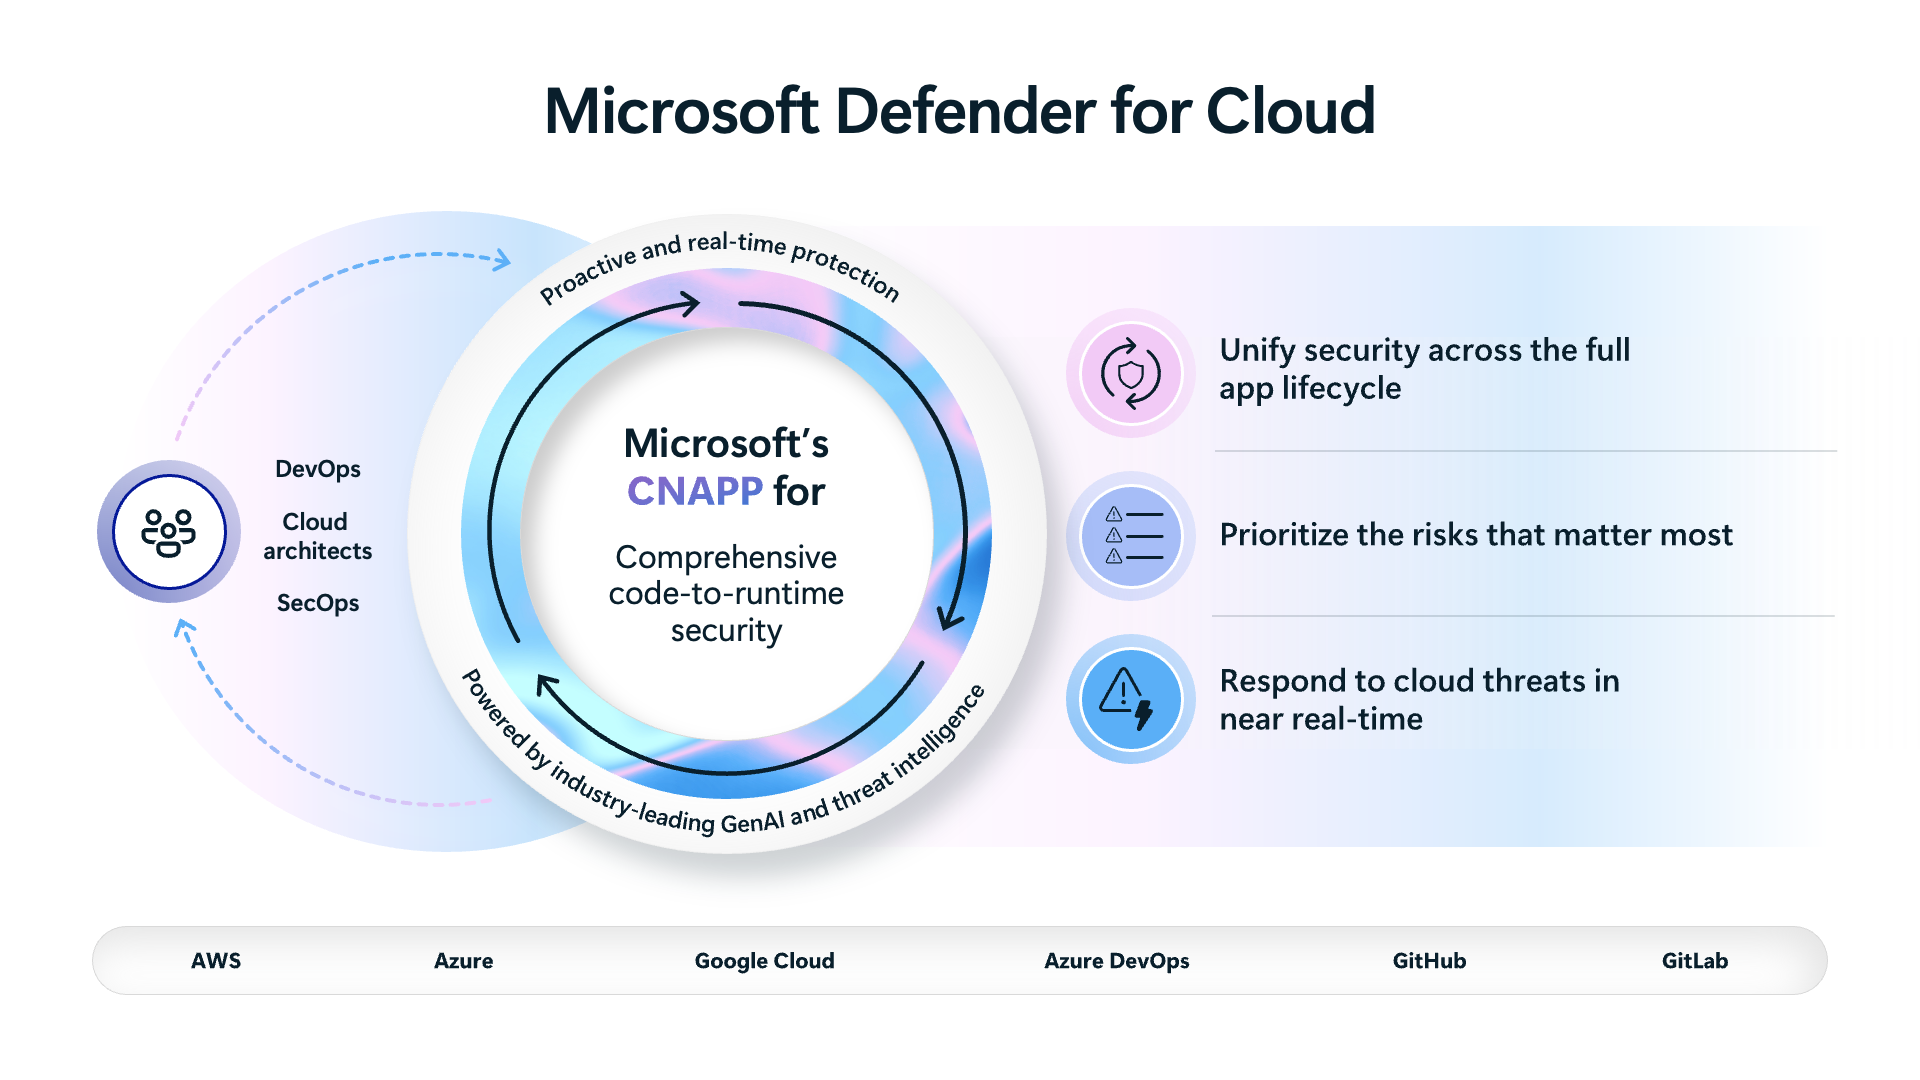 What Defender for Cloud actually is: CNAPP in plain English
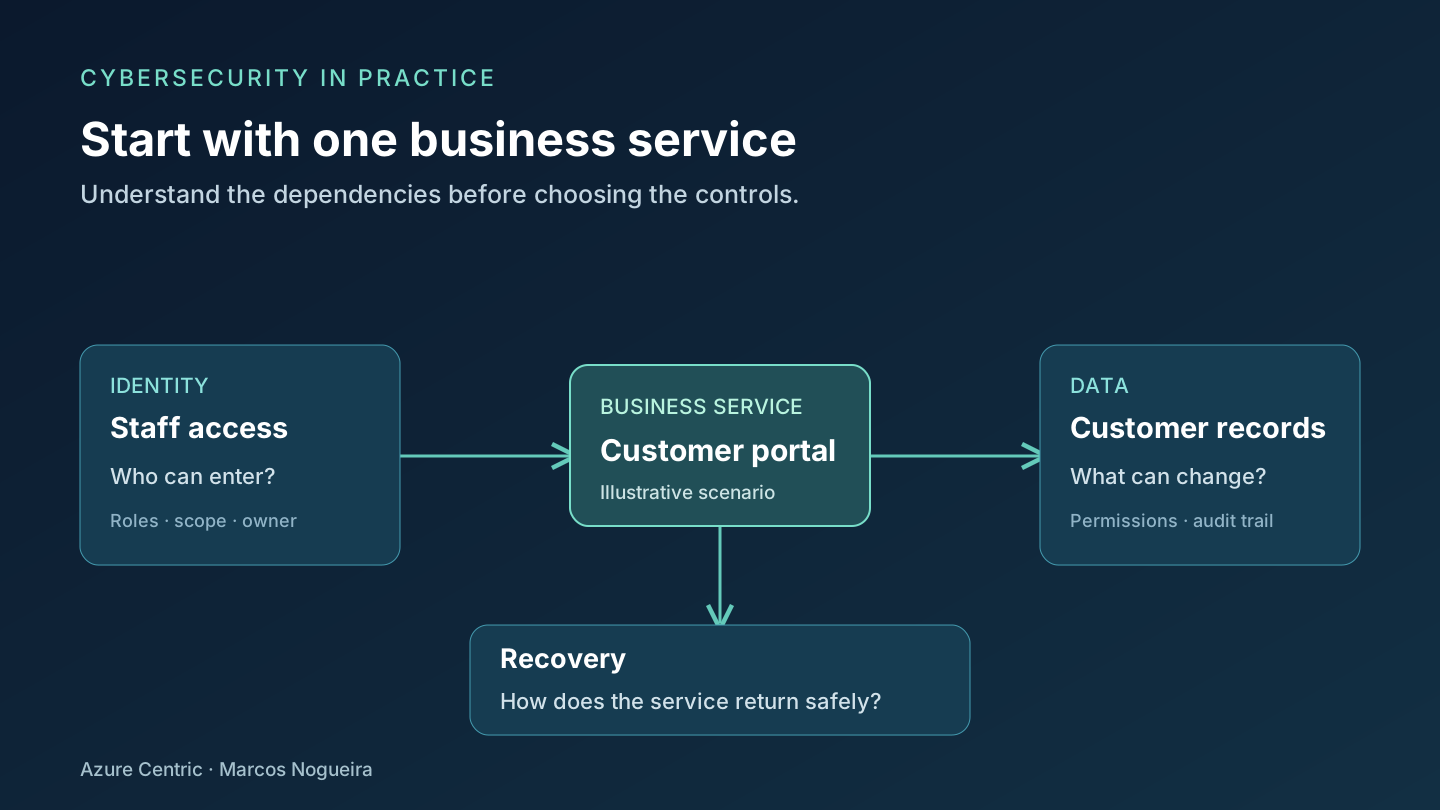 Cybersecurity starts with what your business needs to protect Find gaps between enabled Defender plans and protected resources Build a security review into a new Azure workload Investigate a CodeQL alert before merging a pull request
 Set useful boundaries for security exemptions
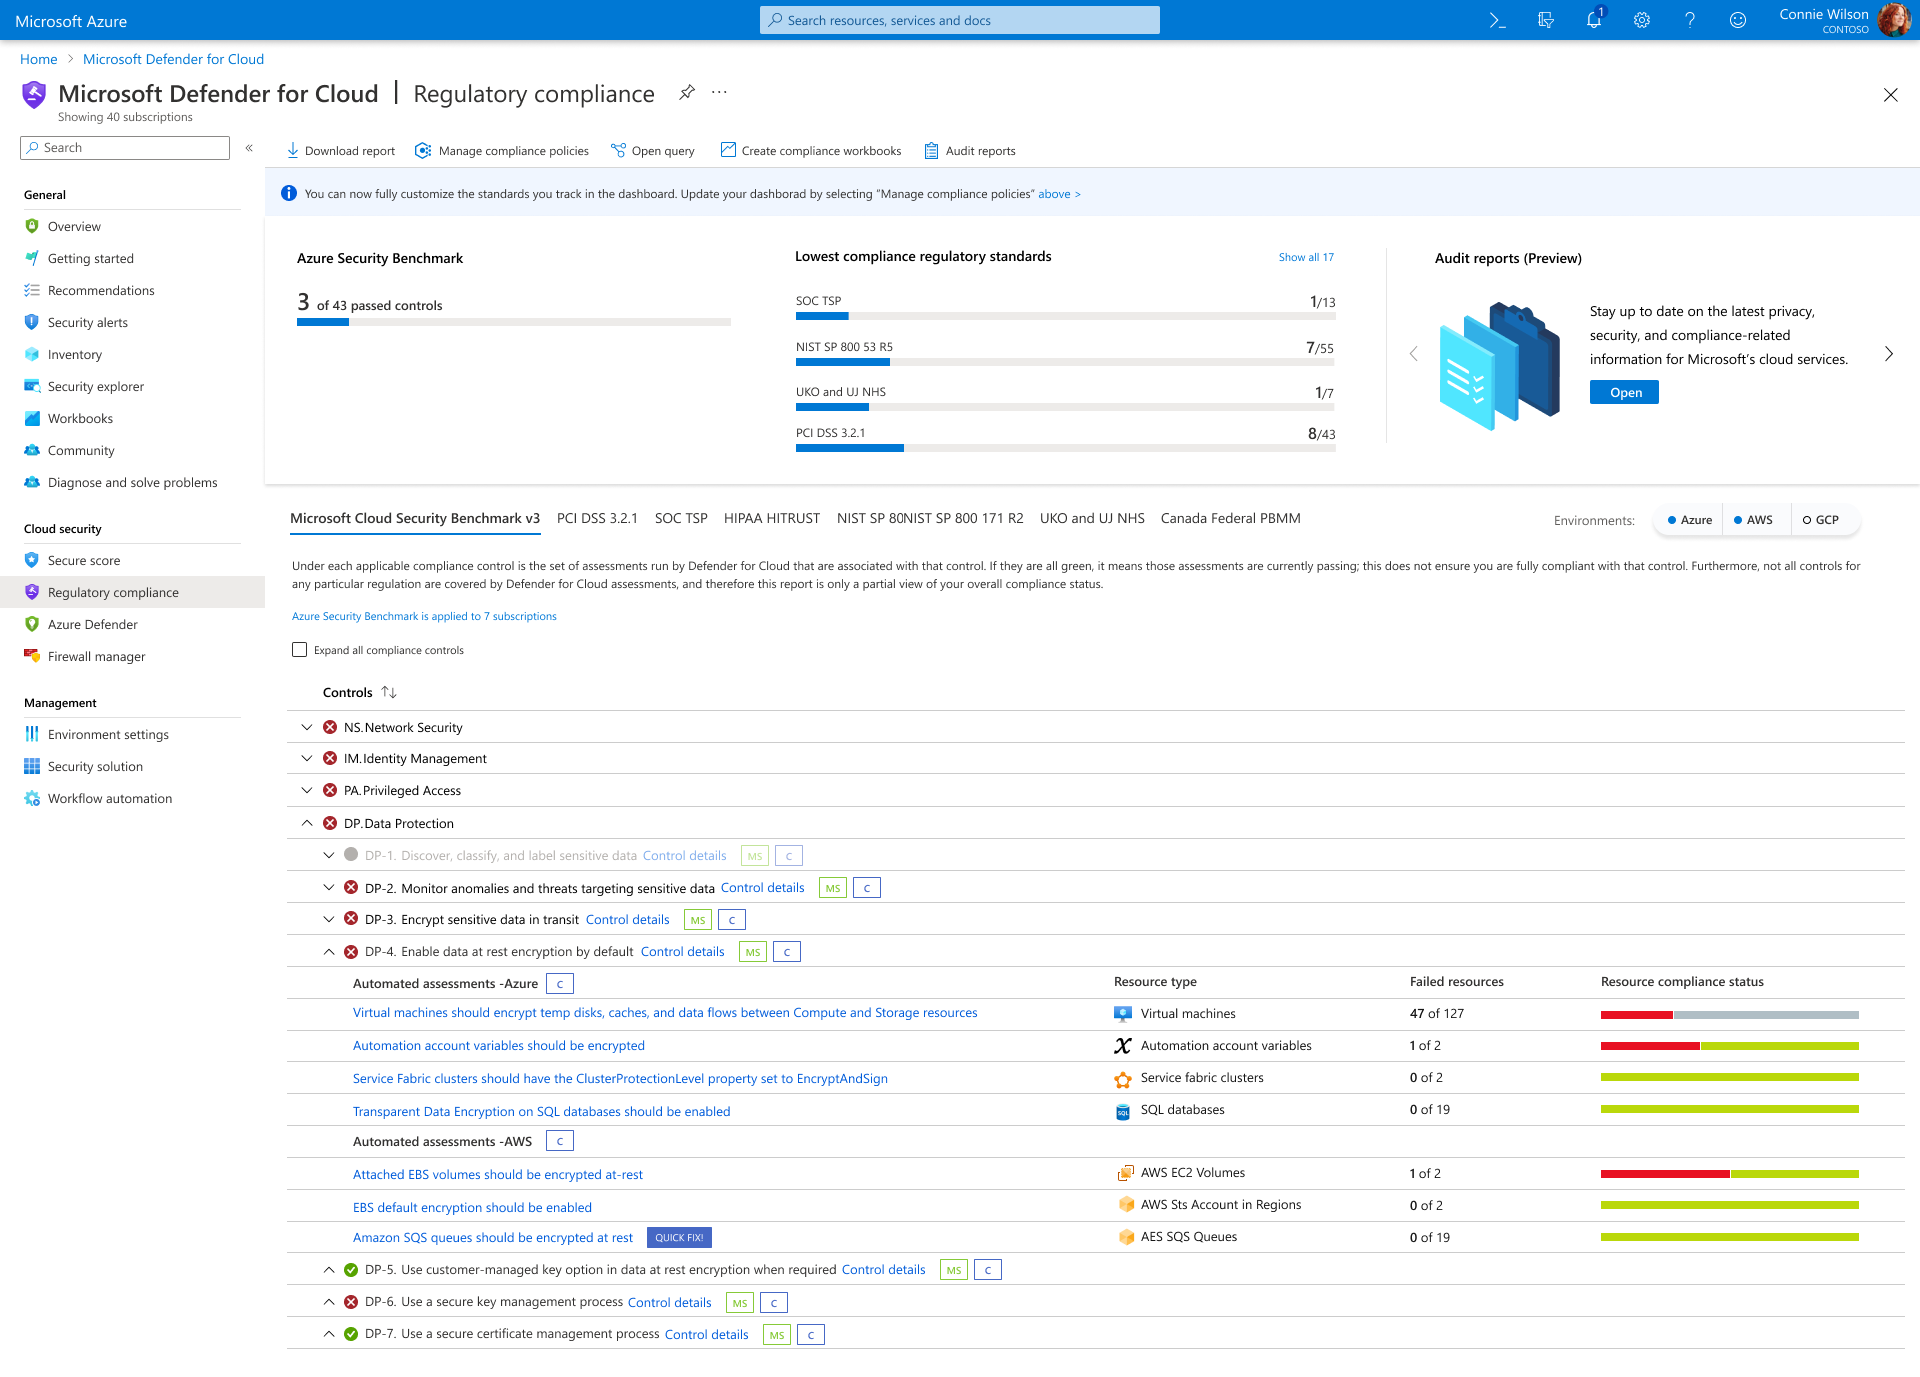 Review the regulatory compliance dashboard in Defender for Cloud Assign owners to cloud security recommendations Choose between network security groups, Azure Firewall and WAF Configure malware scanning for an Azure Storage account
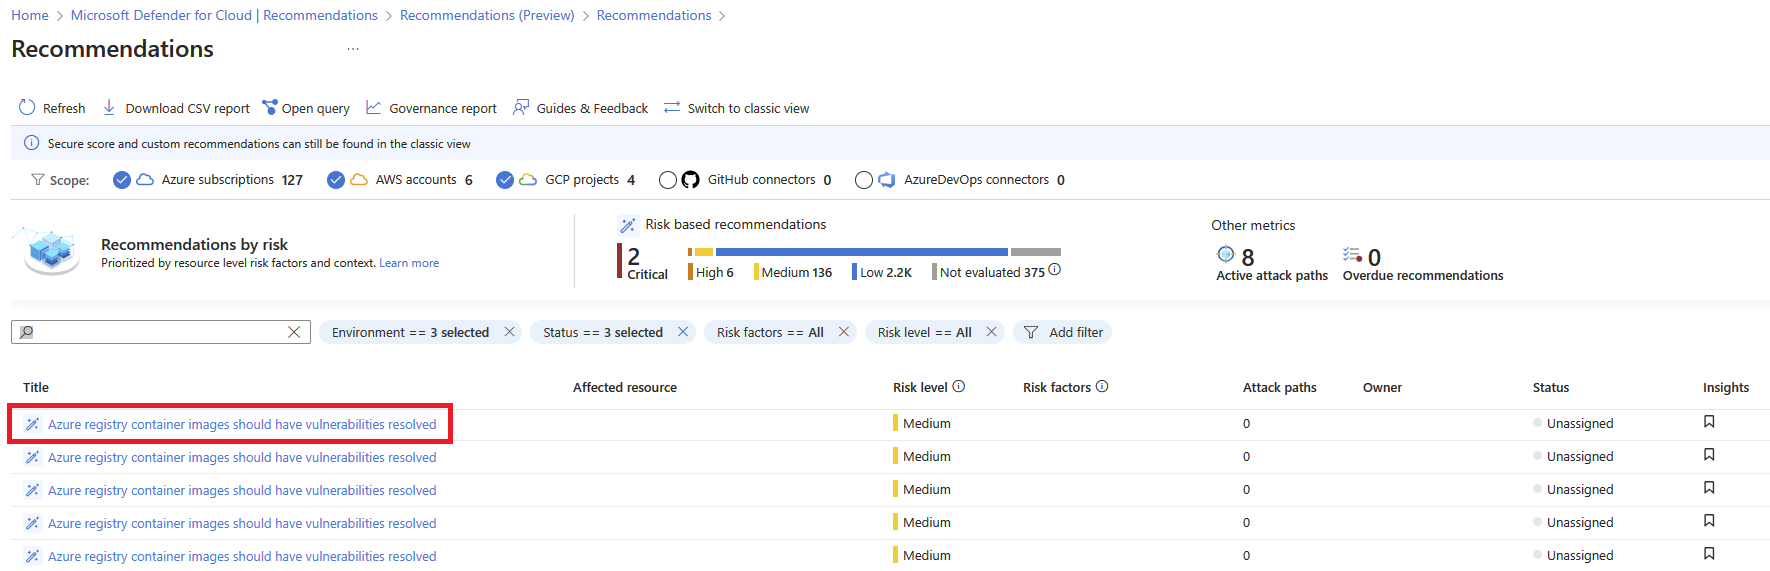 Investigate agentless vulnerability findings before remediation
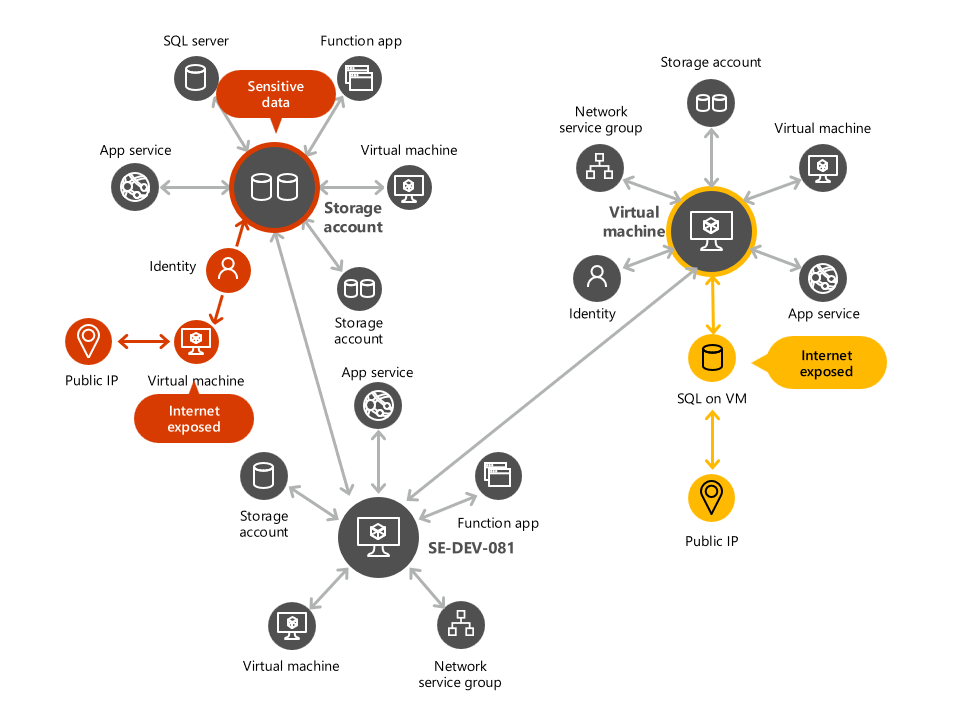 Use attack paths to prioritise exposed Azure resources Review repository protection as GitHub security product choices change
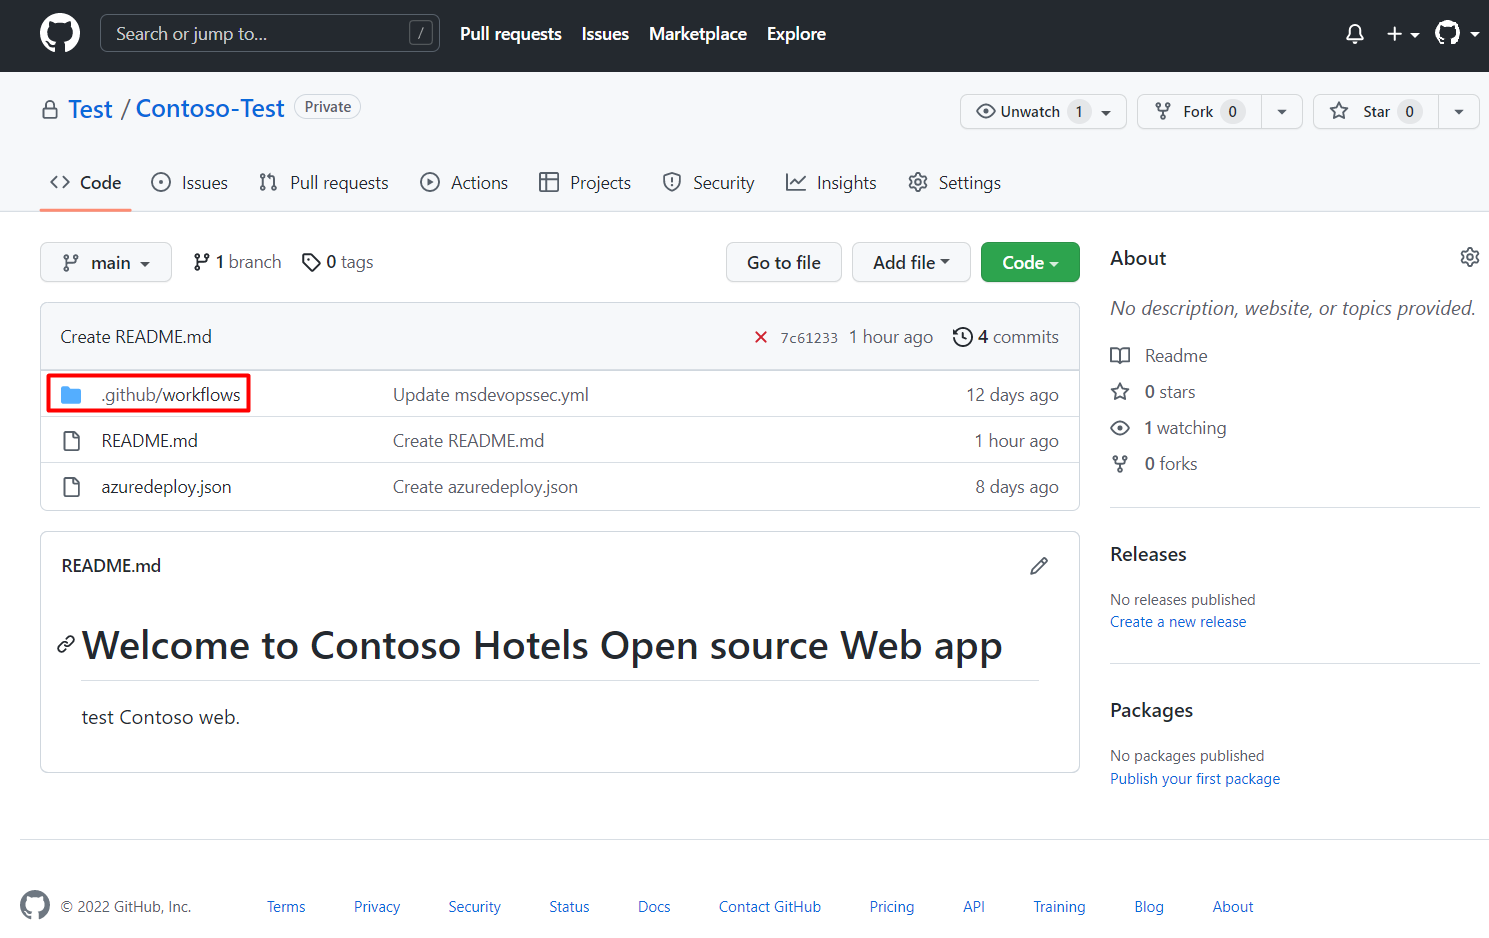 Review infrastructure security findings during a pull request GitHub Code Security and Secret Protection: plan for the new product choices Roll out GitHub push protection without disrupting developers Enable GitHub secret scanning and assign alert ownership Connect GitHub repositories to Defender for Cloud Trace a blocked outbound connection in Azure Firewall logs Keep Azure Firewall rules consistent with Firewall Policy Compare Defender plan coverage across subscriptions
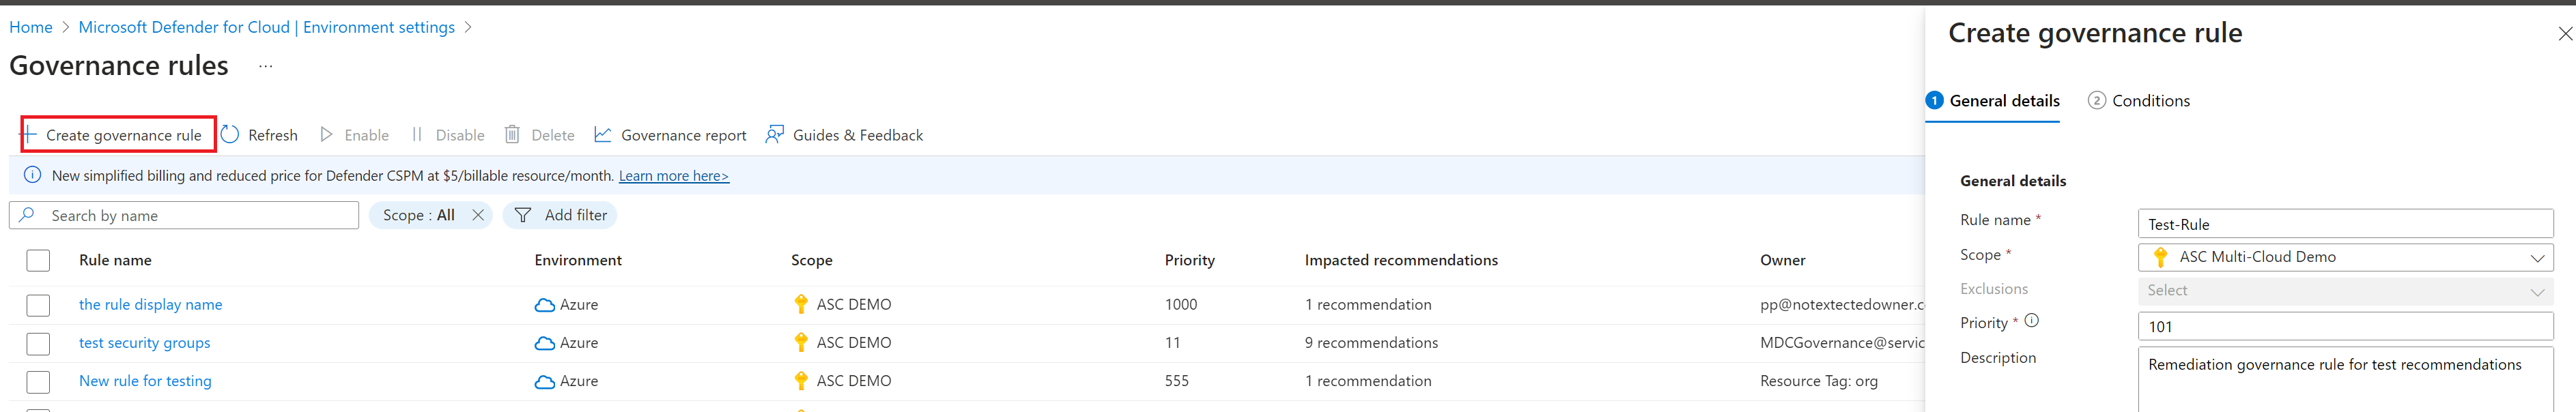
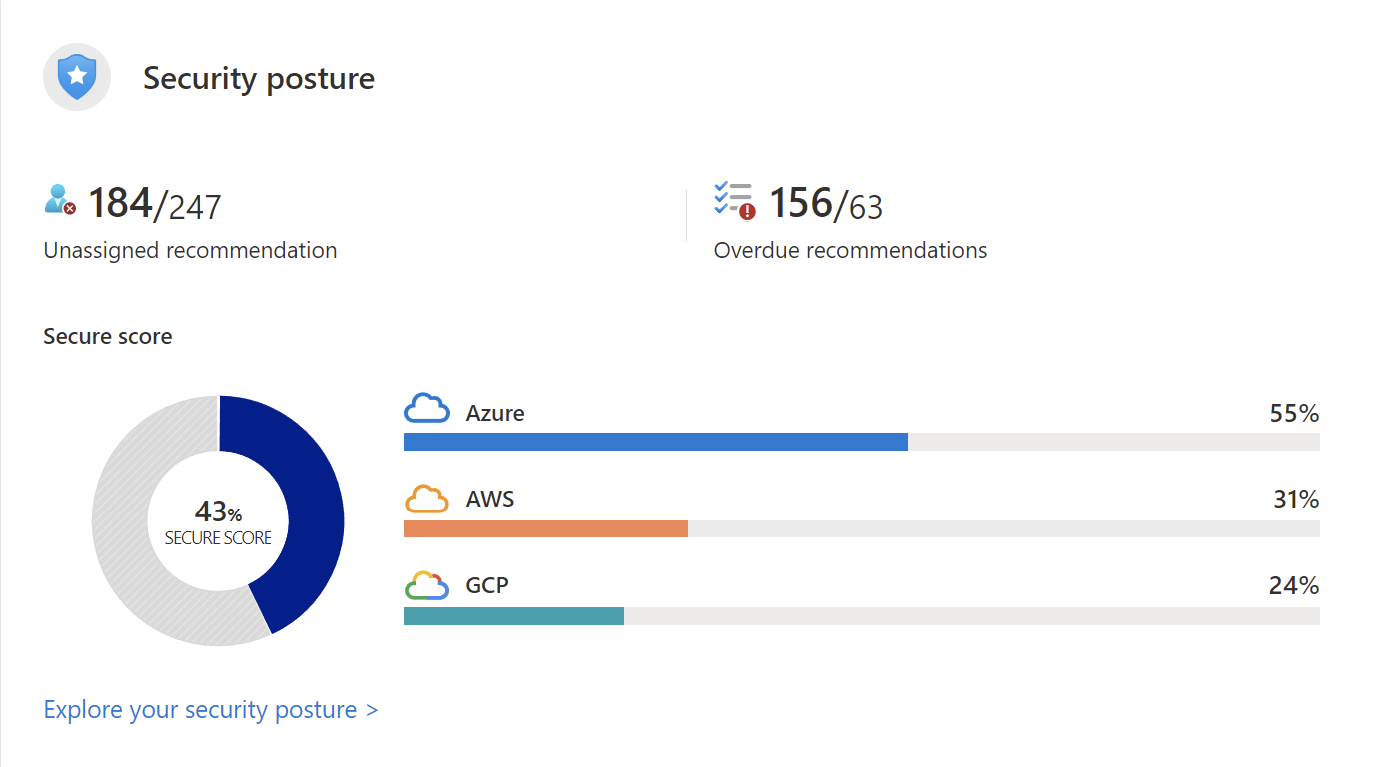 Turn secure score findings into a practical remediation queue
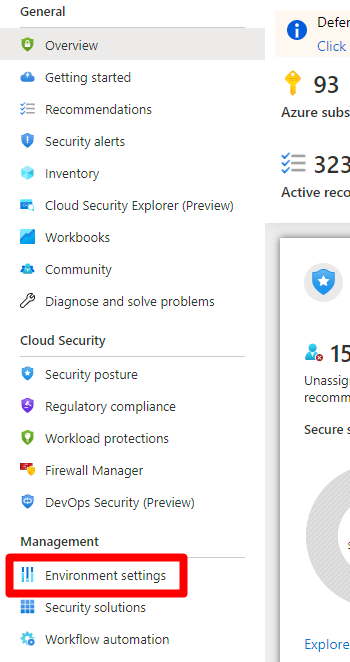 Enable Defender for Cloud with a clear subscription scope
 Understanding the limits on Azure Key Vault How to secure your Azure Virtual Machine