#defender-for-cloud
15 posts, newest first.
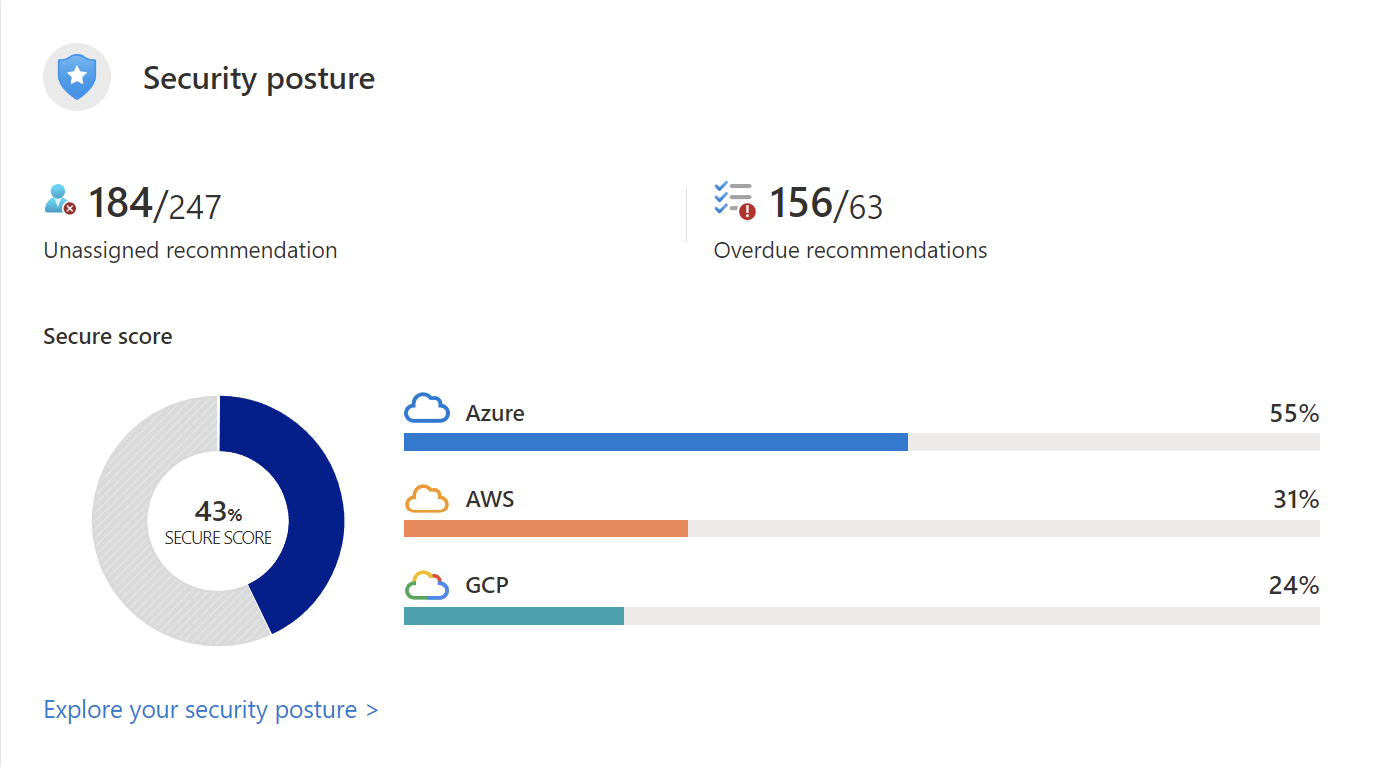 Secure score that drives action, not a weekly percentage
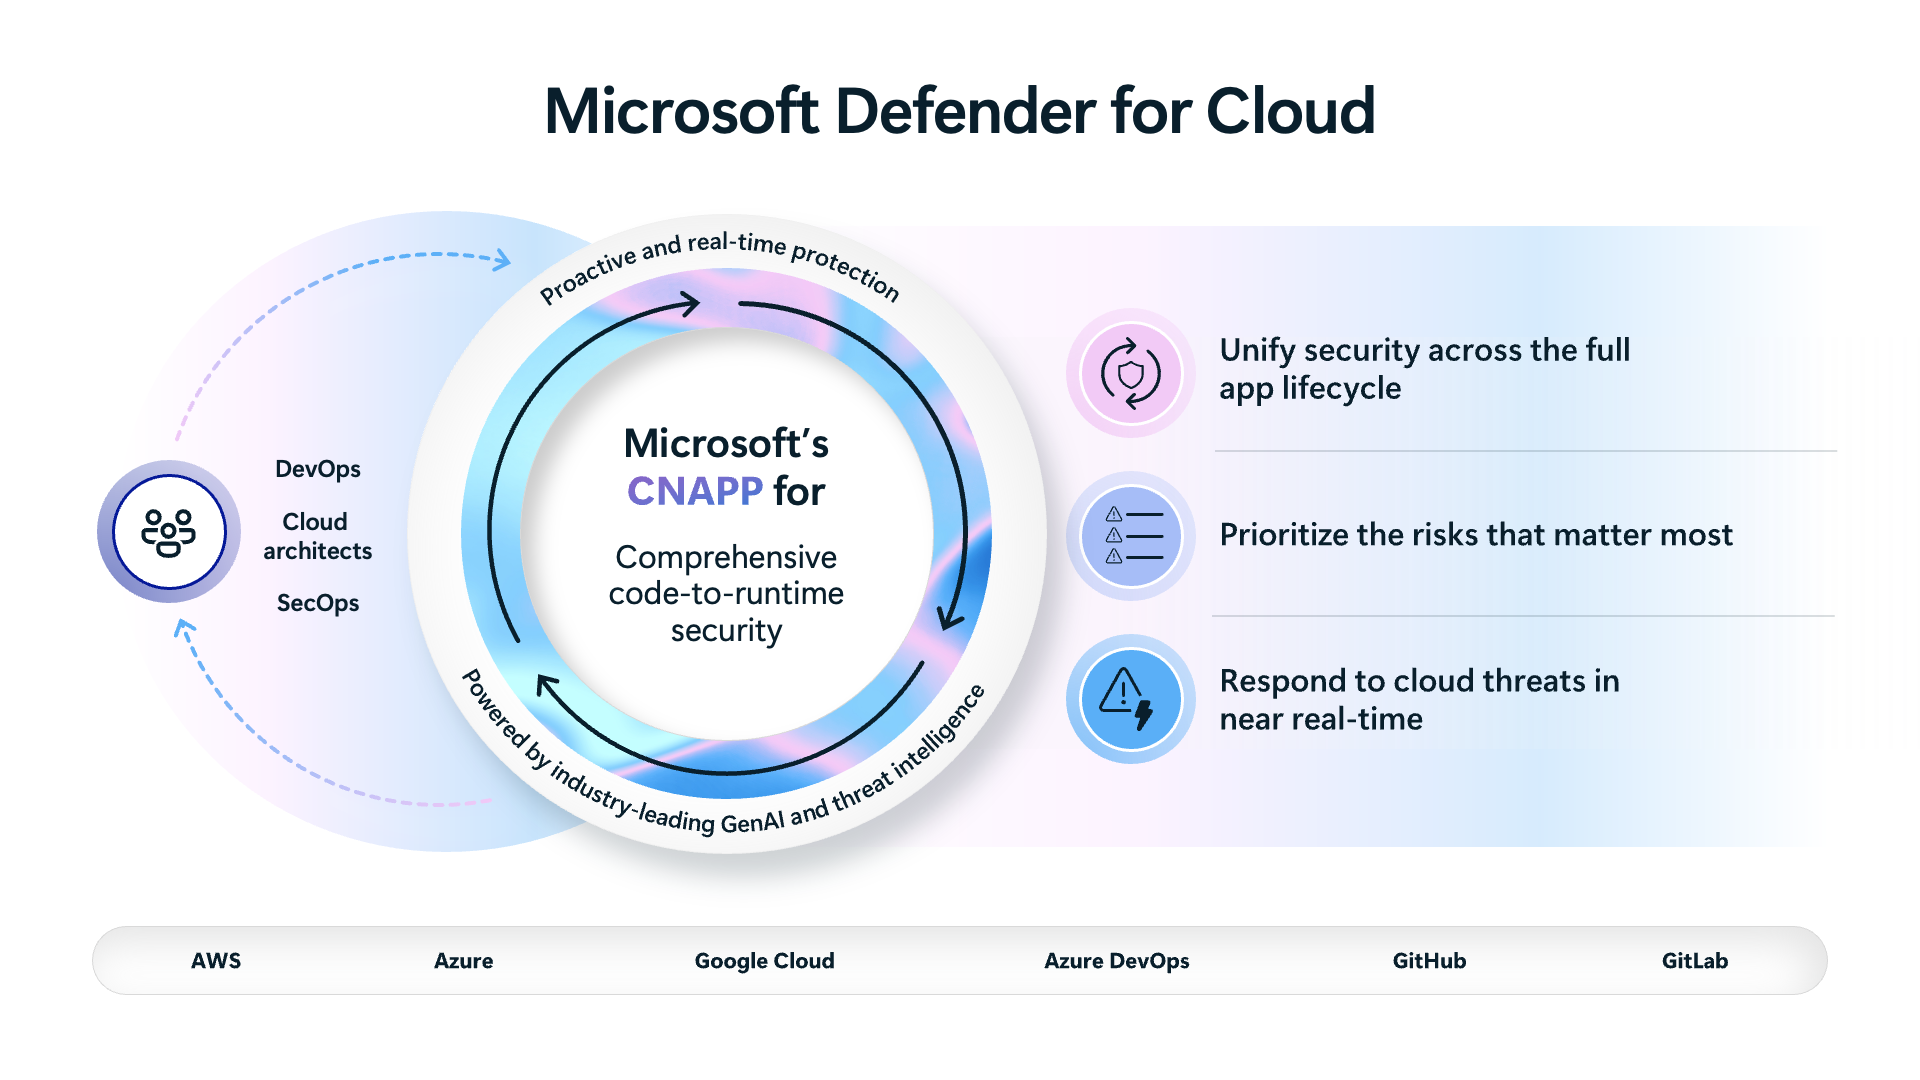 What Defender for Cloud actually is: CNAPP in plain English Find gaps between enabled Defender plans and protected resources Build a security review into a new Azure workload
 Set useful boundaries for security exemptions
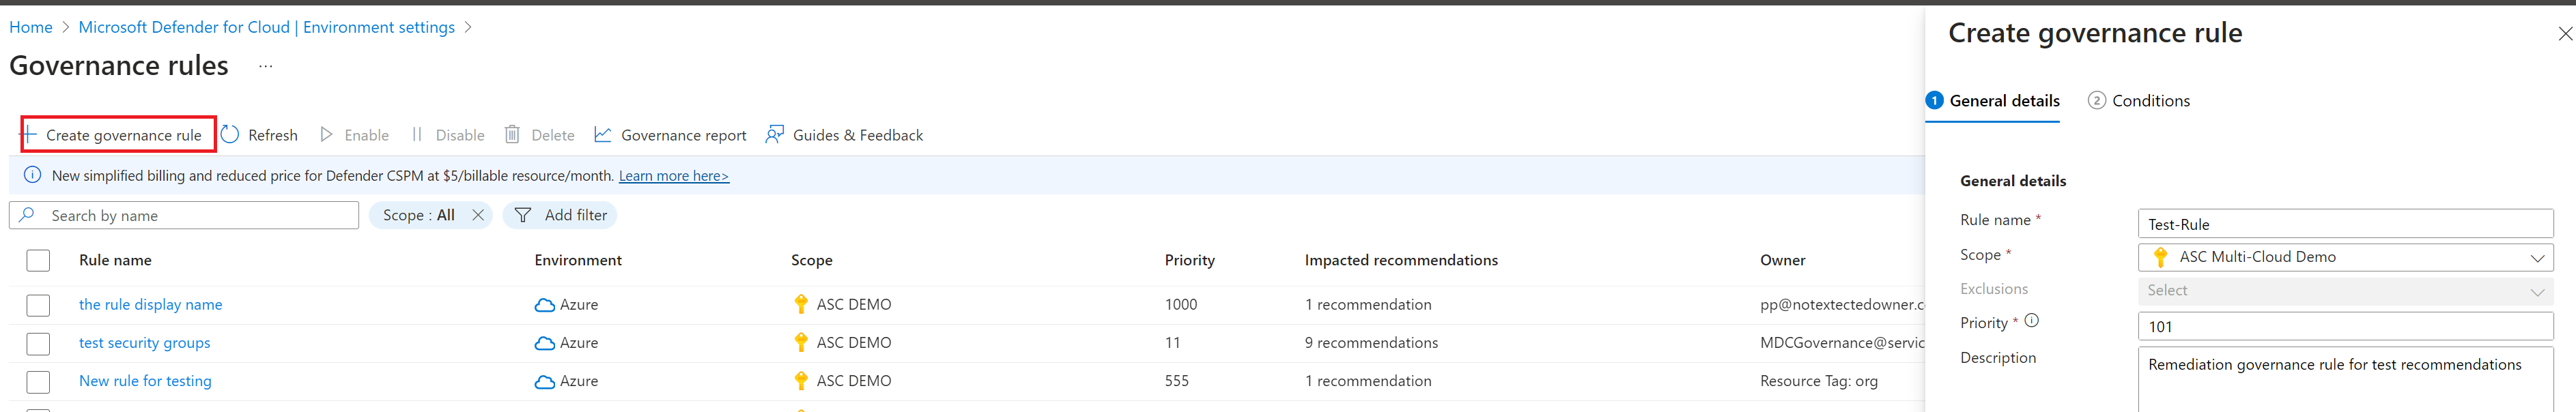
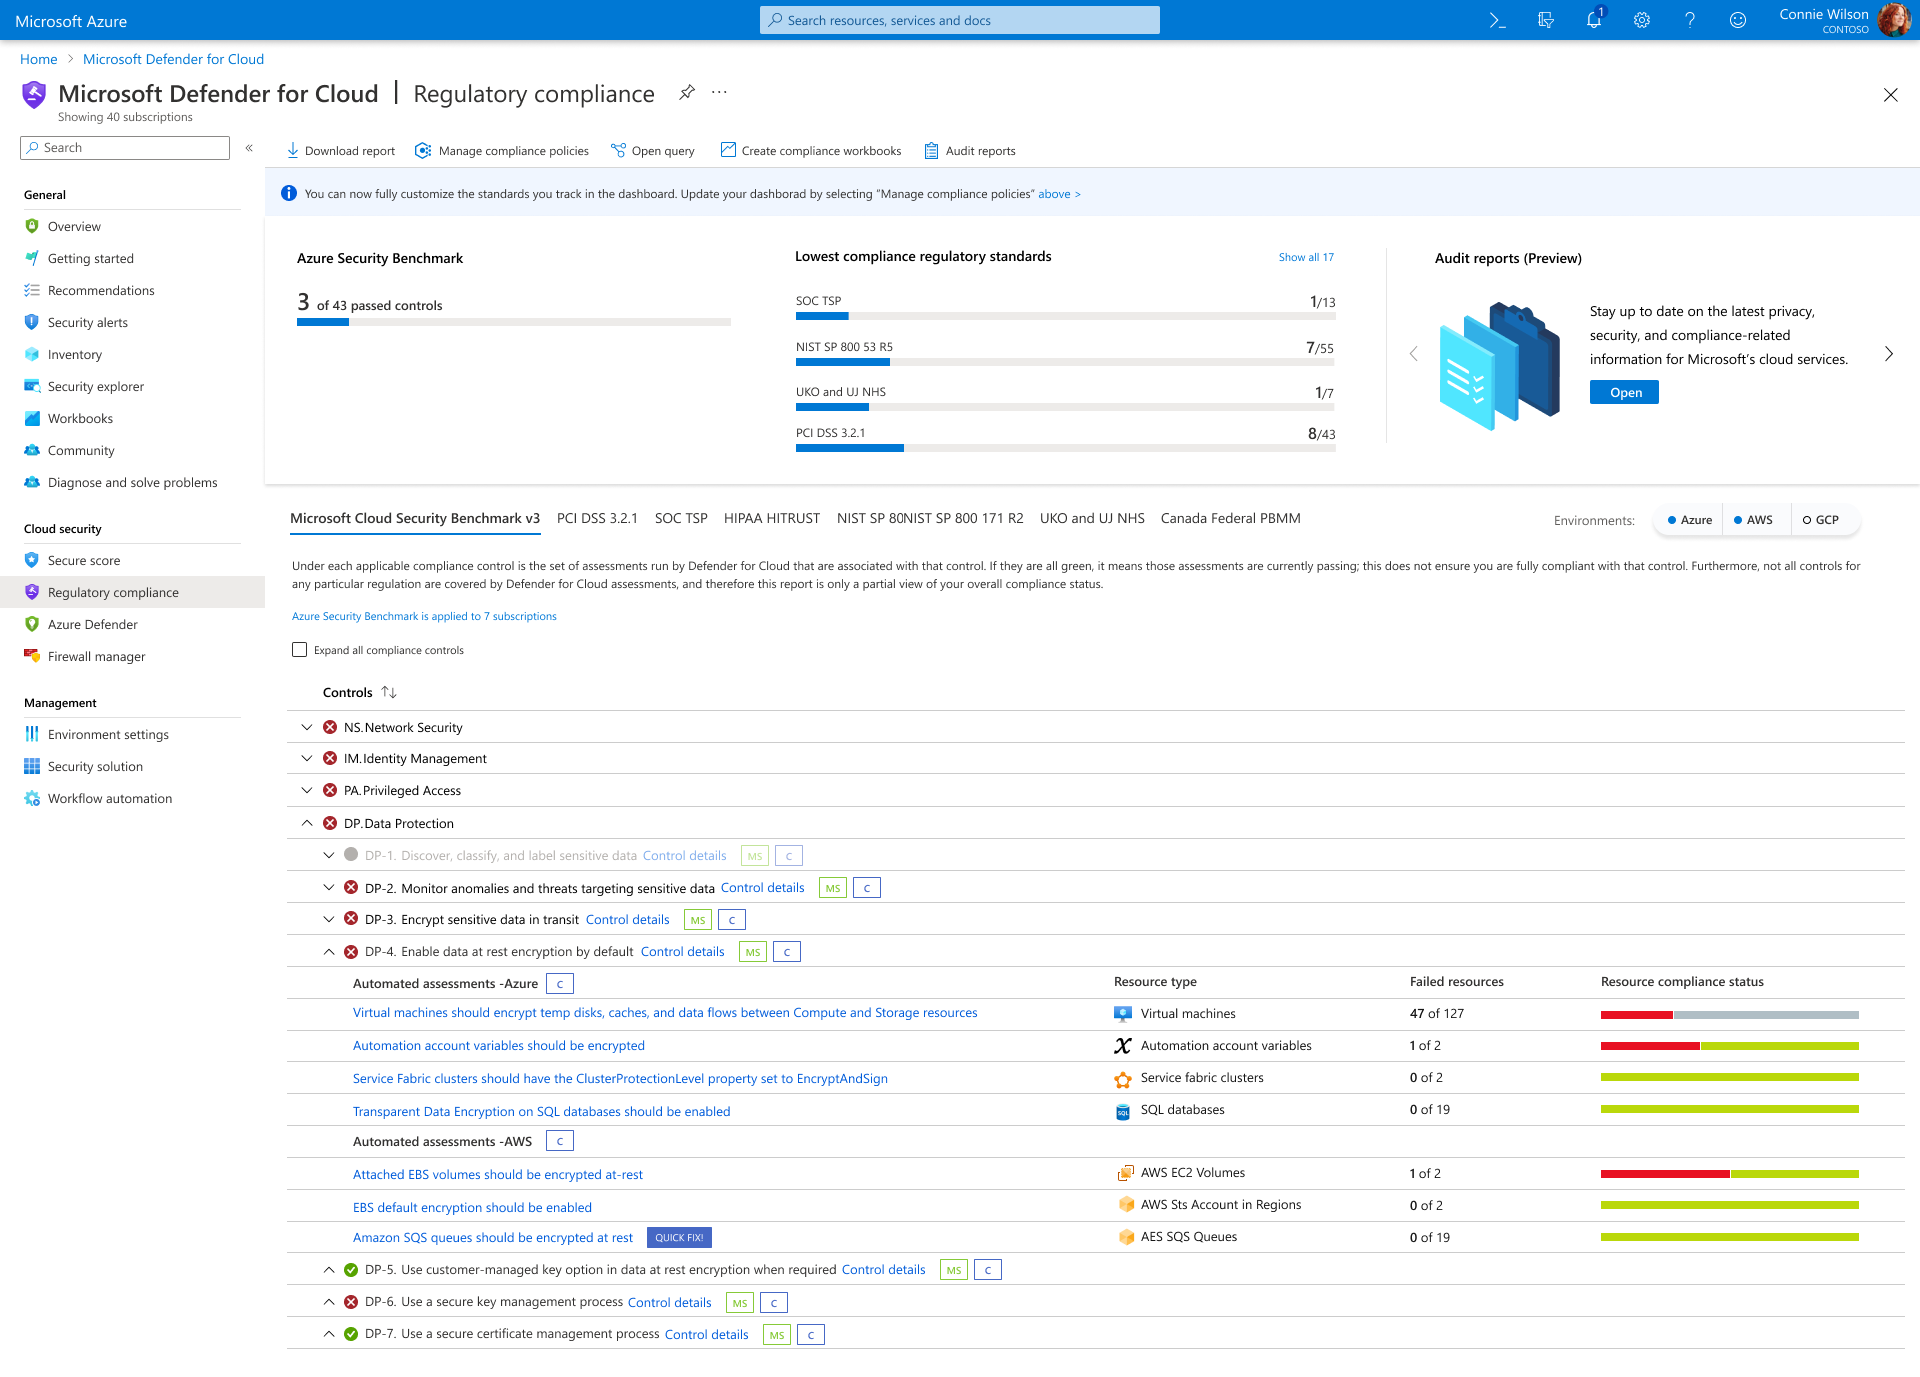 Review the regulatory compliance dashboard in Defender for Cloud Assign owners to cloud security recommendations
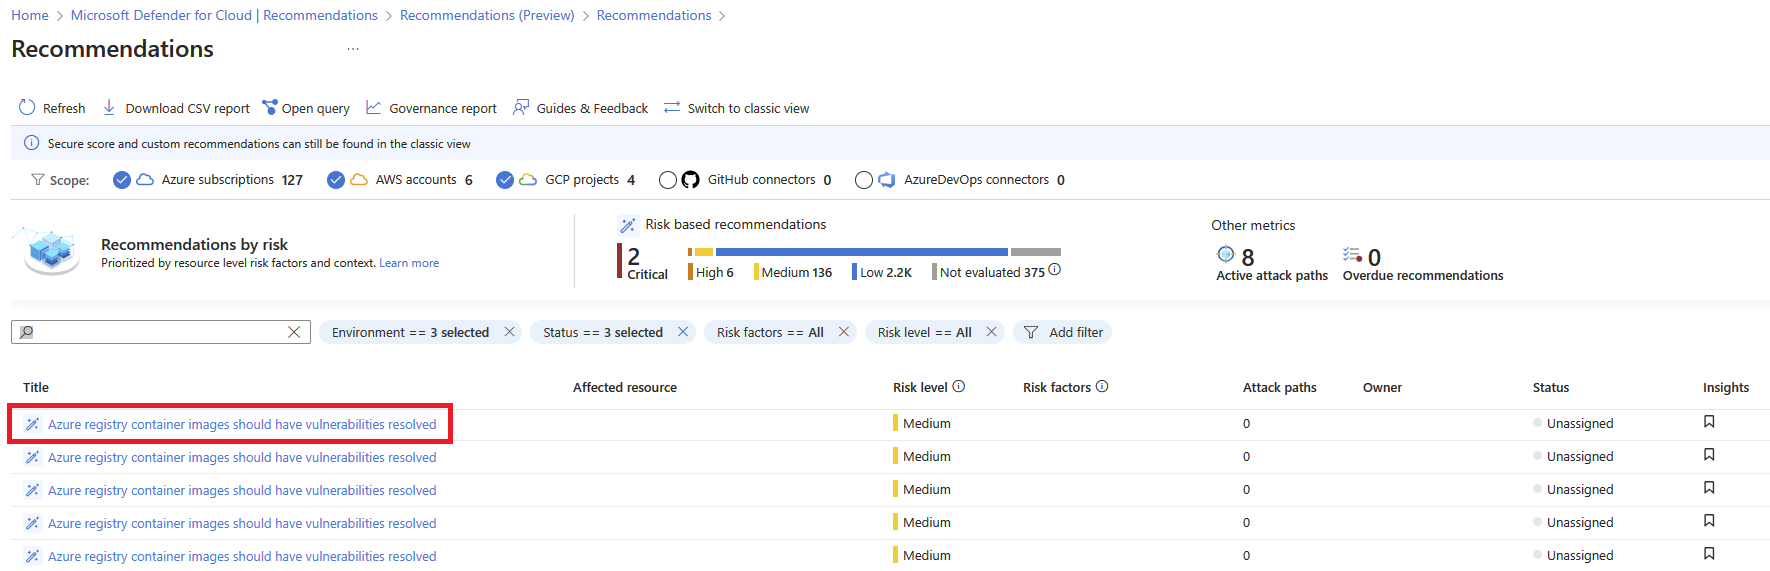 Investigate agentless vulnerability findings before remediation
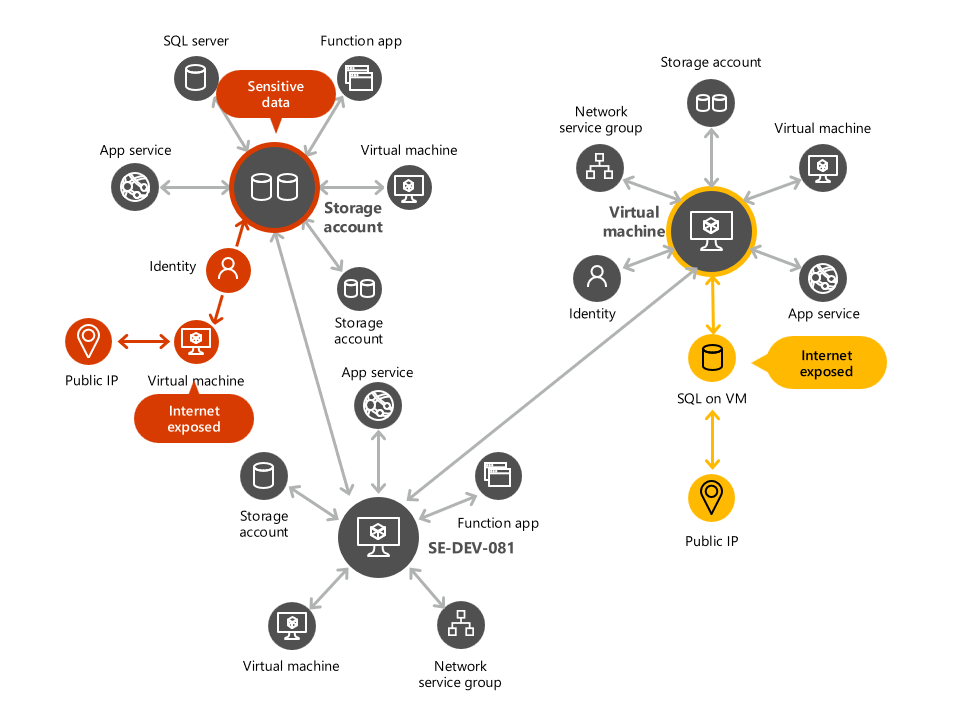 Use attack paths to prioritise exposed Azure resources
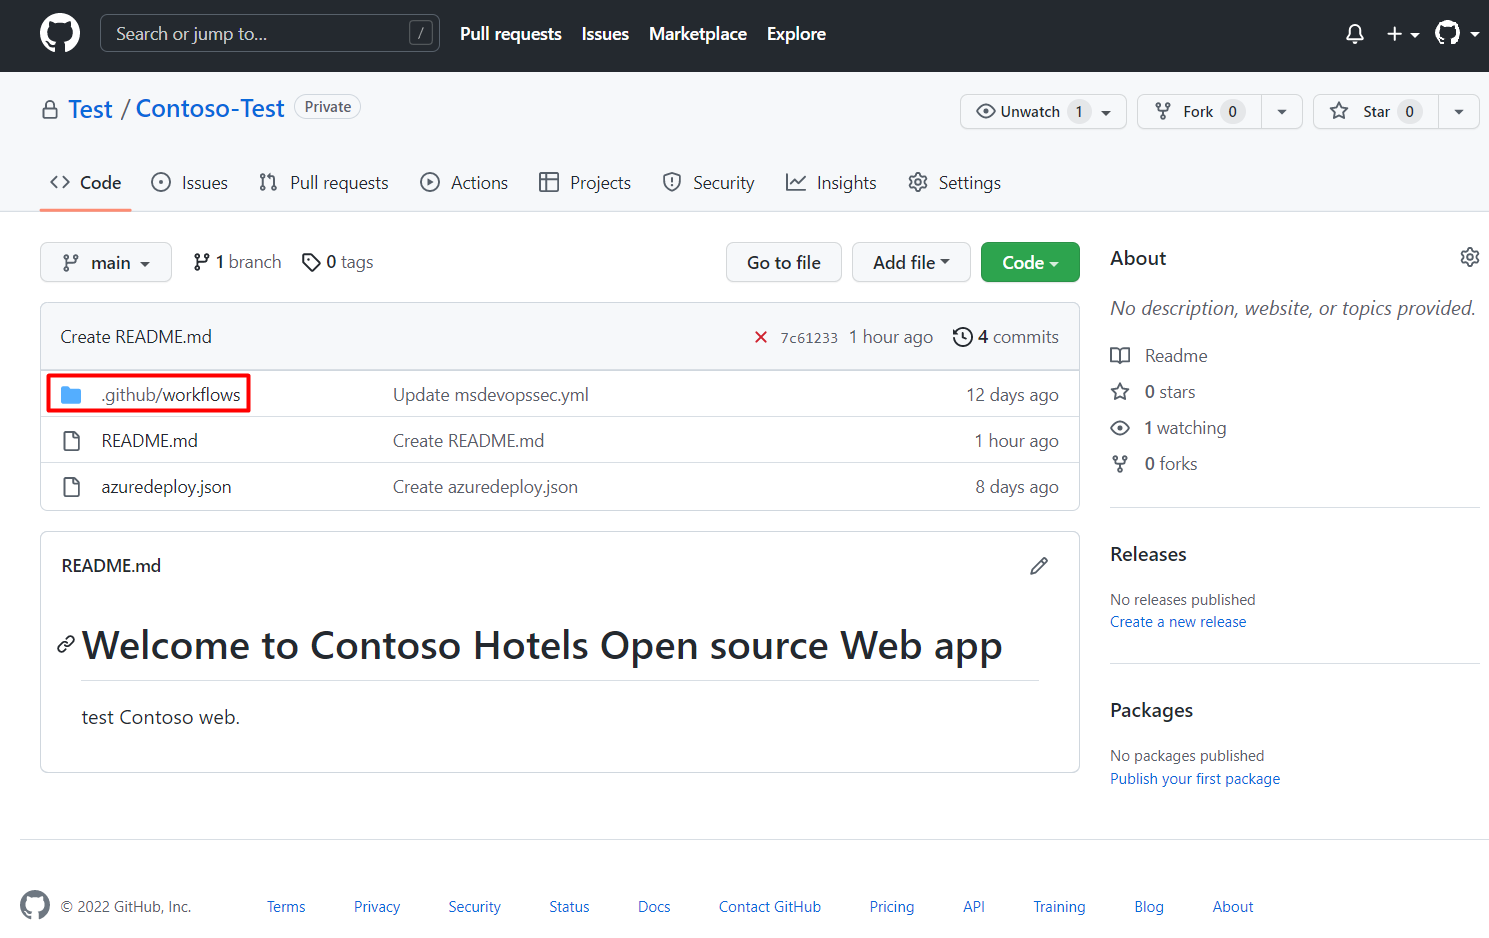 Review infrastructure security findings during a pull request Connect GitHub repositories to Defender for Cloud
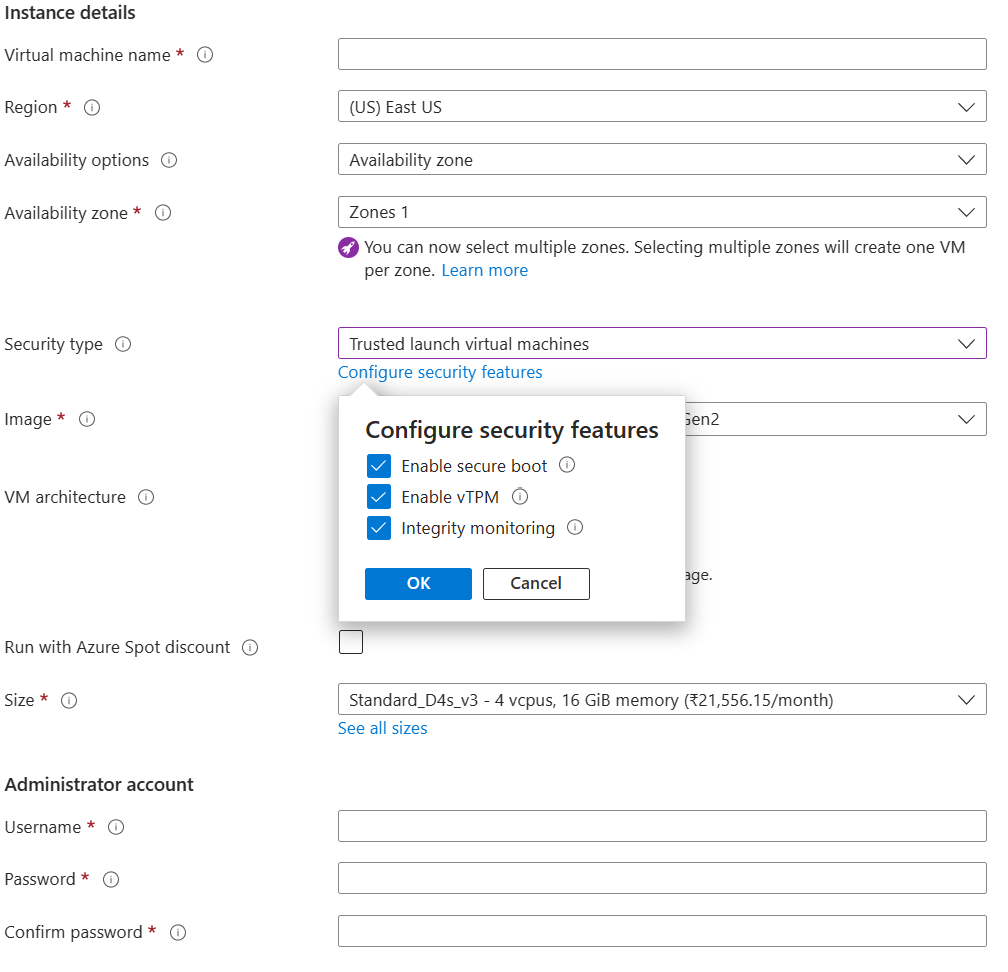 Use Trusted Launch when creating a supported virtual machine Compare Defender plan coverage across subscriptions
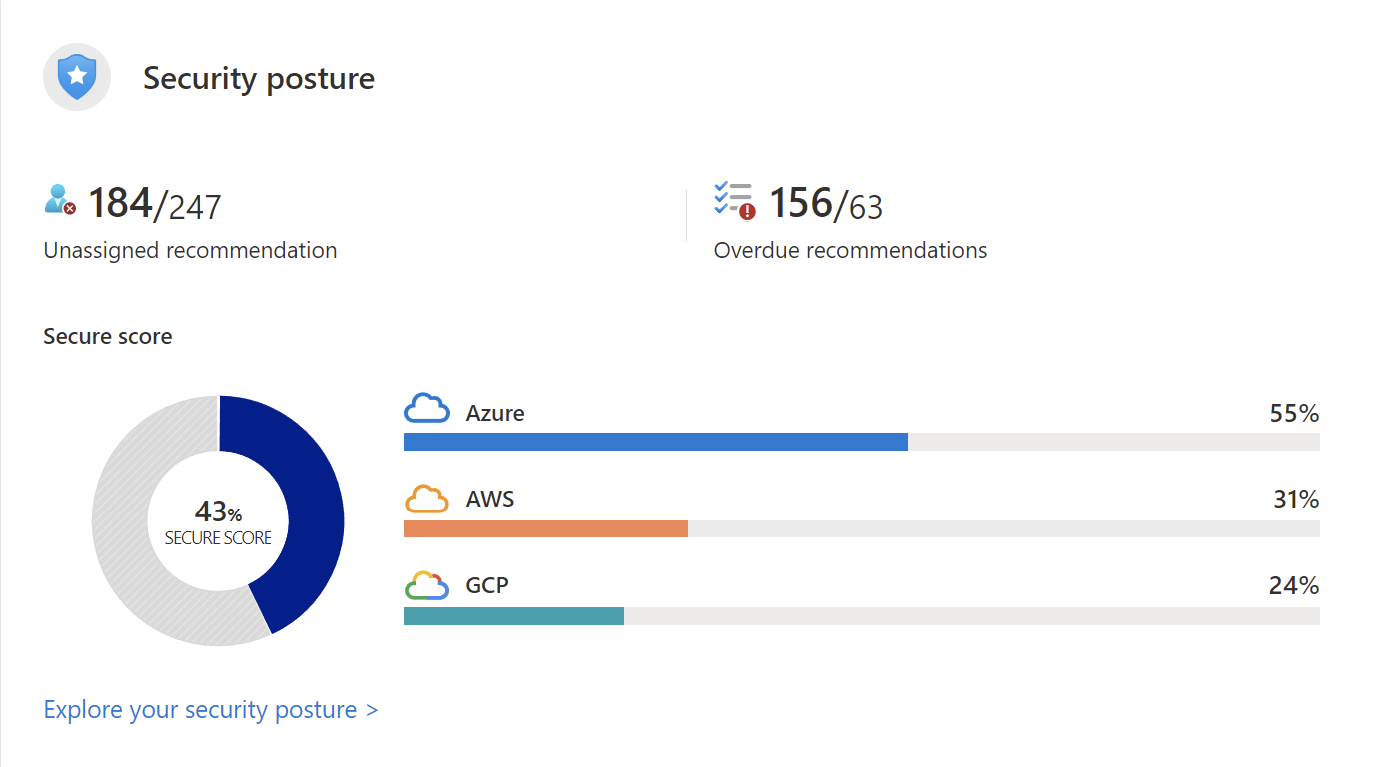 Turn secure score findings into a practical remediation queue
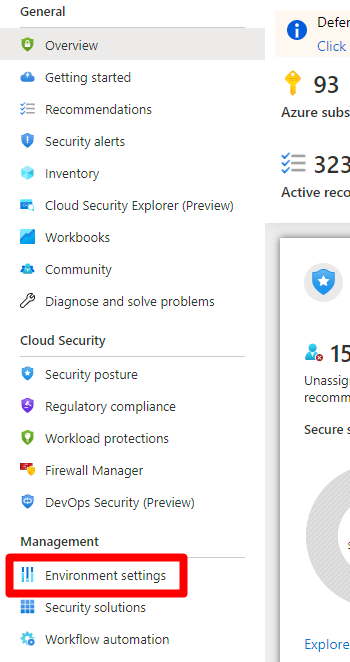 Enable Defender for Cloud with a clear subscription scope