
#alerts
18 posts, newest first.
Review connector health and ingestion changes together 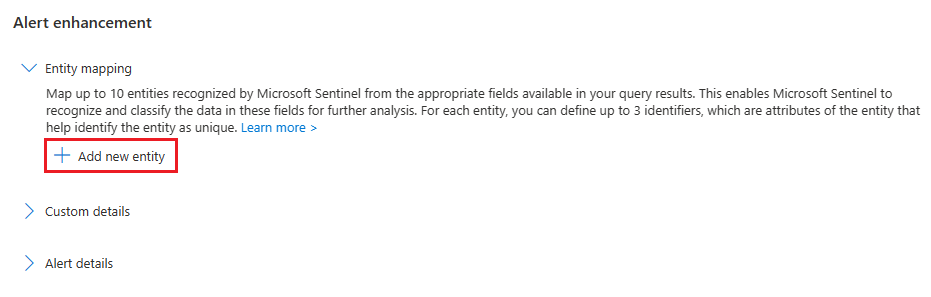 Check entity mapping when related alerts remain separate Investigate a CodeQL alert before merging a pull request
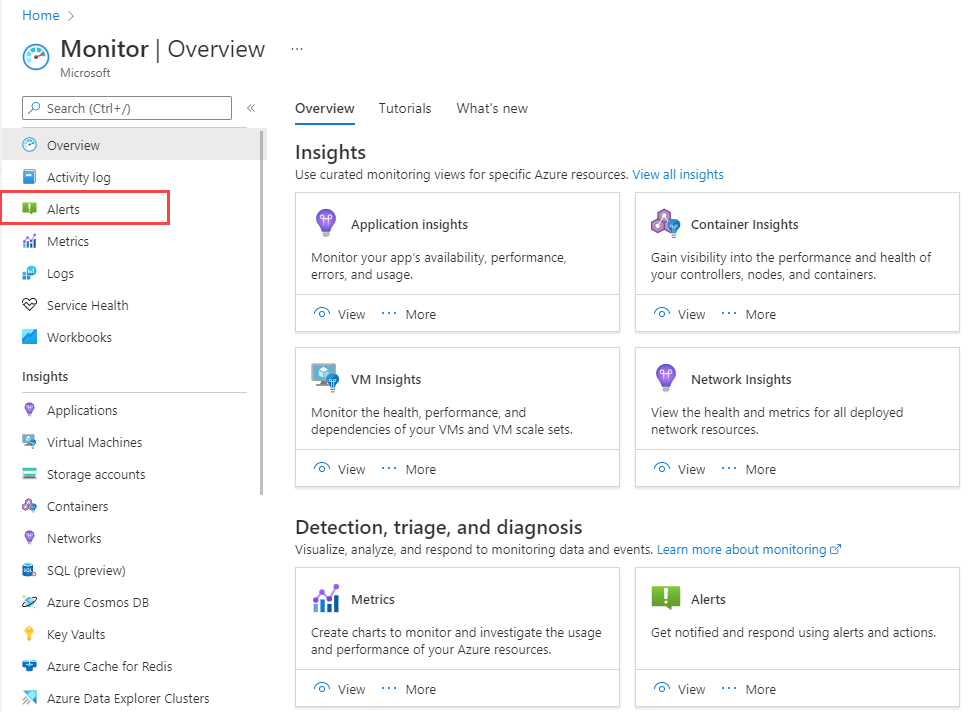 Connect a change record to a useful monitoring check
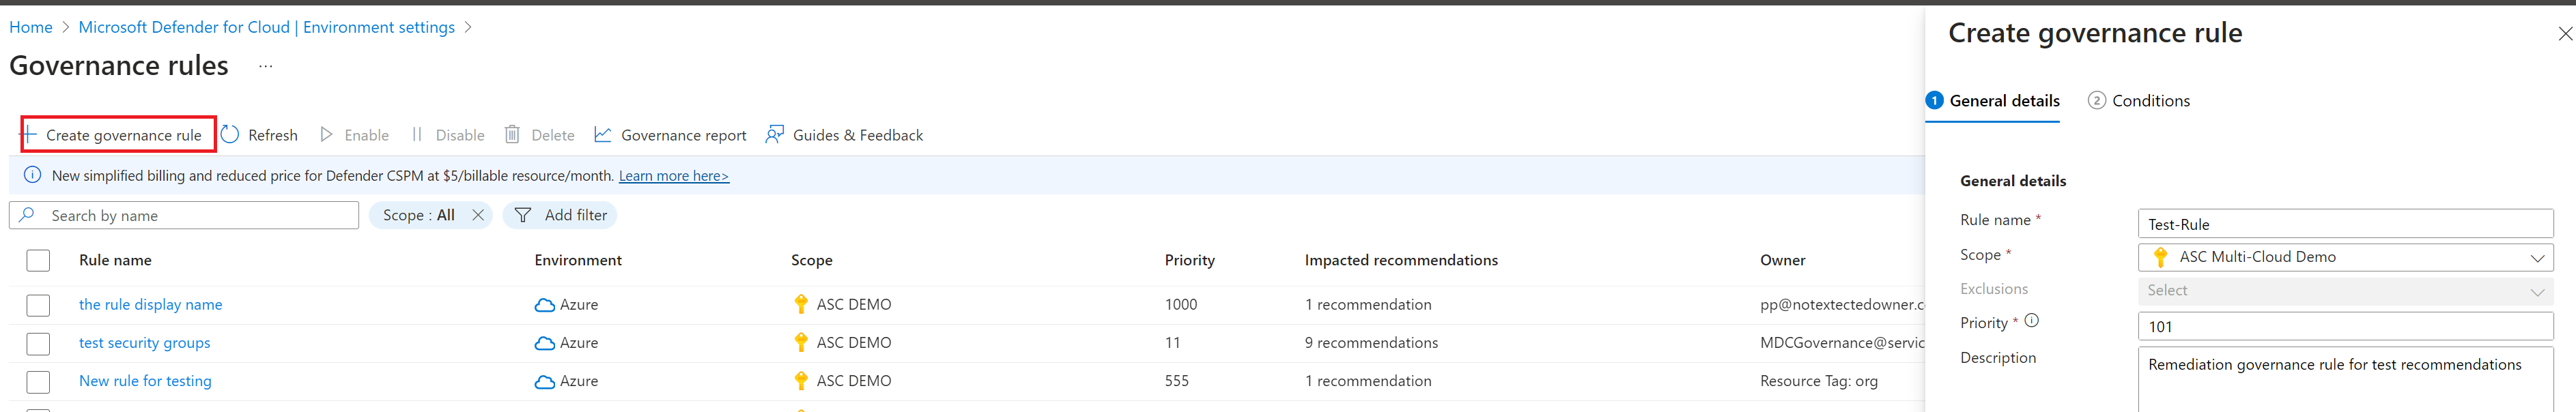 Set useful boundaries for security exemptions Set a budget boundary around a compute experiment Use resource health information during an incident Review event logs around a Windows infrastructure change Investigate an alert that repeatedly closes and reopens
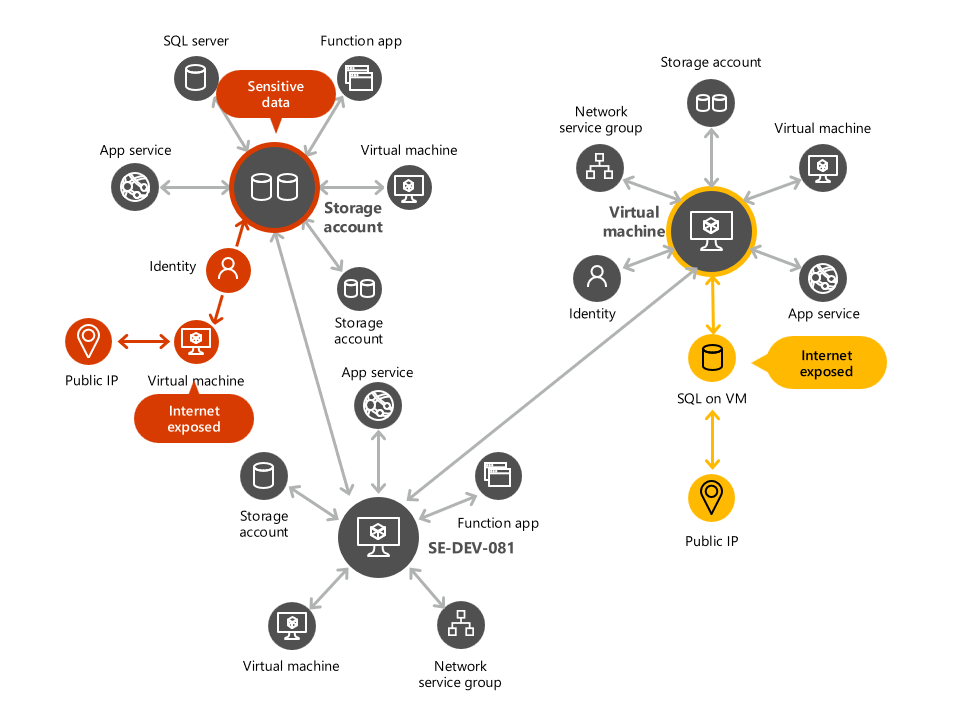 Use attack paths to prioritise exposed Azure resources Choose alert thresholds around an actionable response Enable GitHub secret scanning and assign alert ownership Investigate a Windows service that fails after a restart Troubleshoot a Sentinel connector that stopped sending data What Copilot for Security can help a security team investigate Build an Azure Monitor alert with a useful action group
 Multiple level alerts with ARM Template SCOM Alert: WinRM is not functional or not the right version
 Check entity mapping when related alerts remain separate Investigate a CodeQL alert before merging a pull request Connect a change record to a useful monitoring check Set useful boundaries for security exemptions Set a budget boundary around a compute experiment Use resource health information during an incident Review event logs around a Windows infrastructure change Investigate an alert that repeatedly closes and reopens Use attack paths to prioritise exposed Azure resources Choose alert thresholds around an actionable response Enable GitHub secret scanning and assign alert ownership Investigate a Windows service that fails after a restart Troubleshoot a Sentinel connector that stopped sending data What Copilot for Security can help a security team investigate Build an Azure Monitor alert with a useful action group Multiple level alerts with ARM Template SCOM Alert: WinRM is not functional or not the right version