
SIEM & XDR
19 posts, newest first.
#advanced-hunting#alerts#analytics-rules#automation#automation-rules#azure-logic-apps#azure-monitor#azure-monitor-agent#configuration#content-hub#cost-management#data-collection-rules#data-connectors#data-retention#detection-tuning#entity-mapping#false-positives#incident-correlation#incident-triage#kql#log-analytics#microsoft-defender-xdr#microsoft-sentinel#migration#monitoring#playbooks#rbac#security-operations#threat-detection#threat-hunting#threat-intelligence#threat-investigation#troubleshooting#tuning#watchlists#windows-security
Review connector health and ingestion changes together 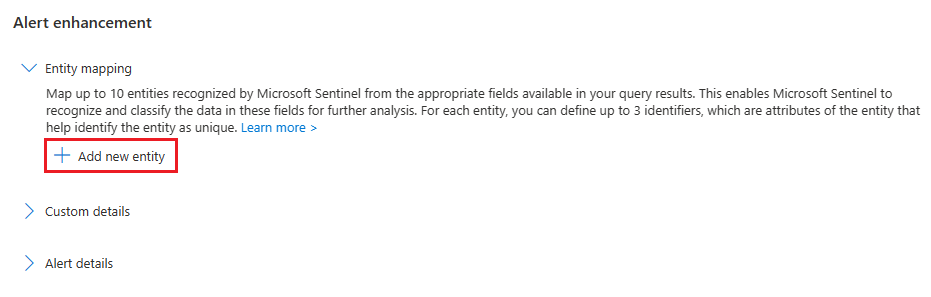 Check entity mapping when related alerts remain separate
 All posts in this category
Build an incident triage workbook for the operations team 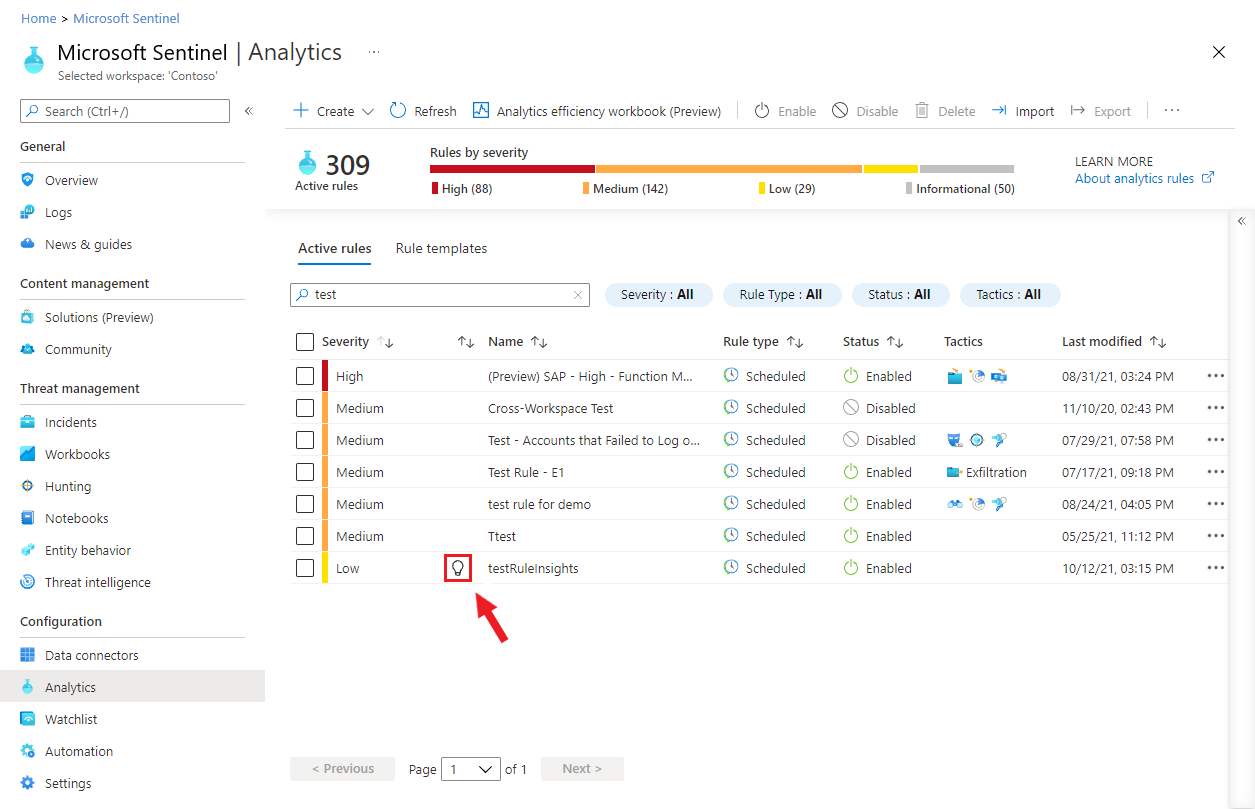 Choose a detection exclusion or a rule change
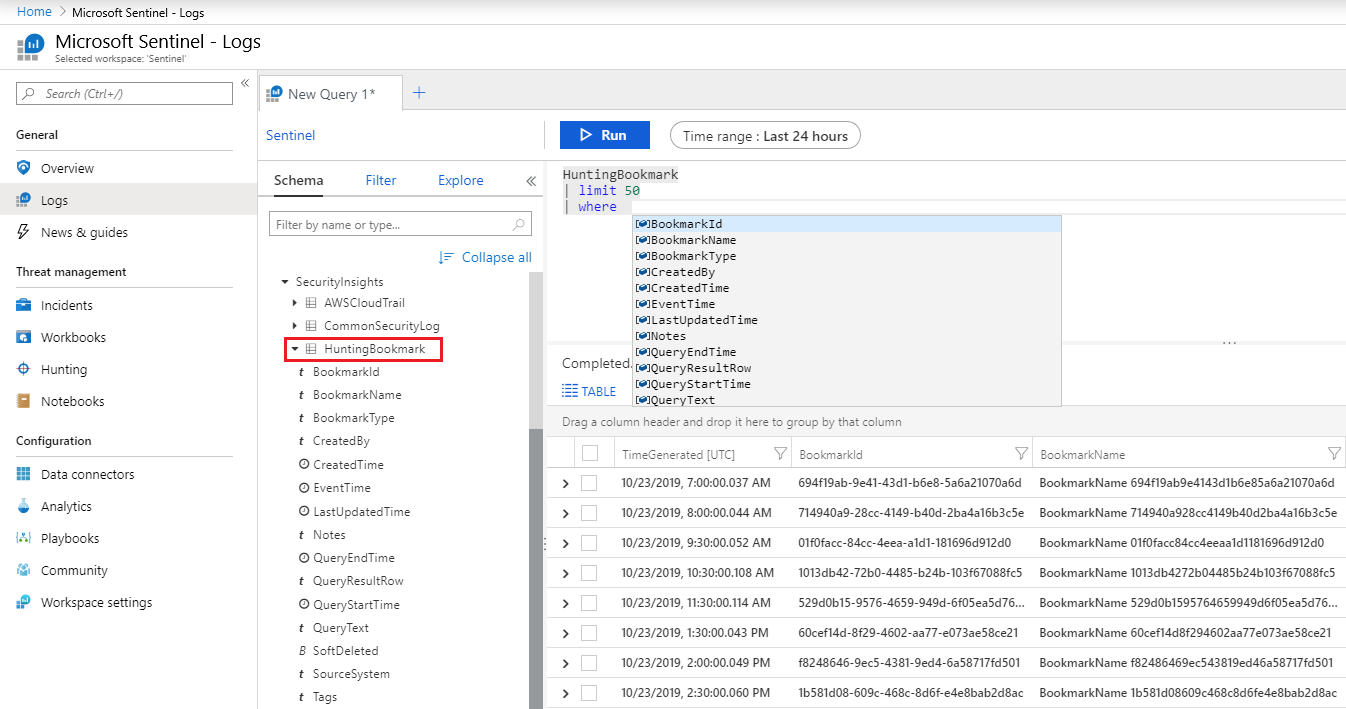 Use Advanced Hunting to test a Defender XDR hypothesis Connect Sentinel incidents with Defender XDR context Investigate a rule that creates too many incidents
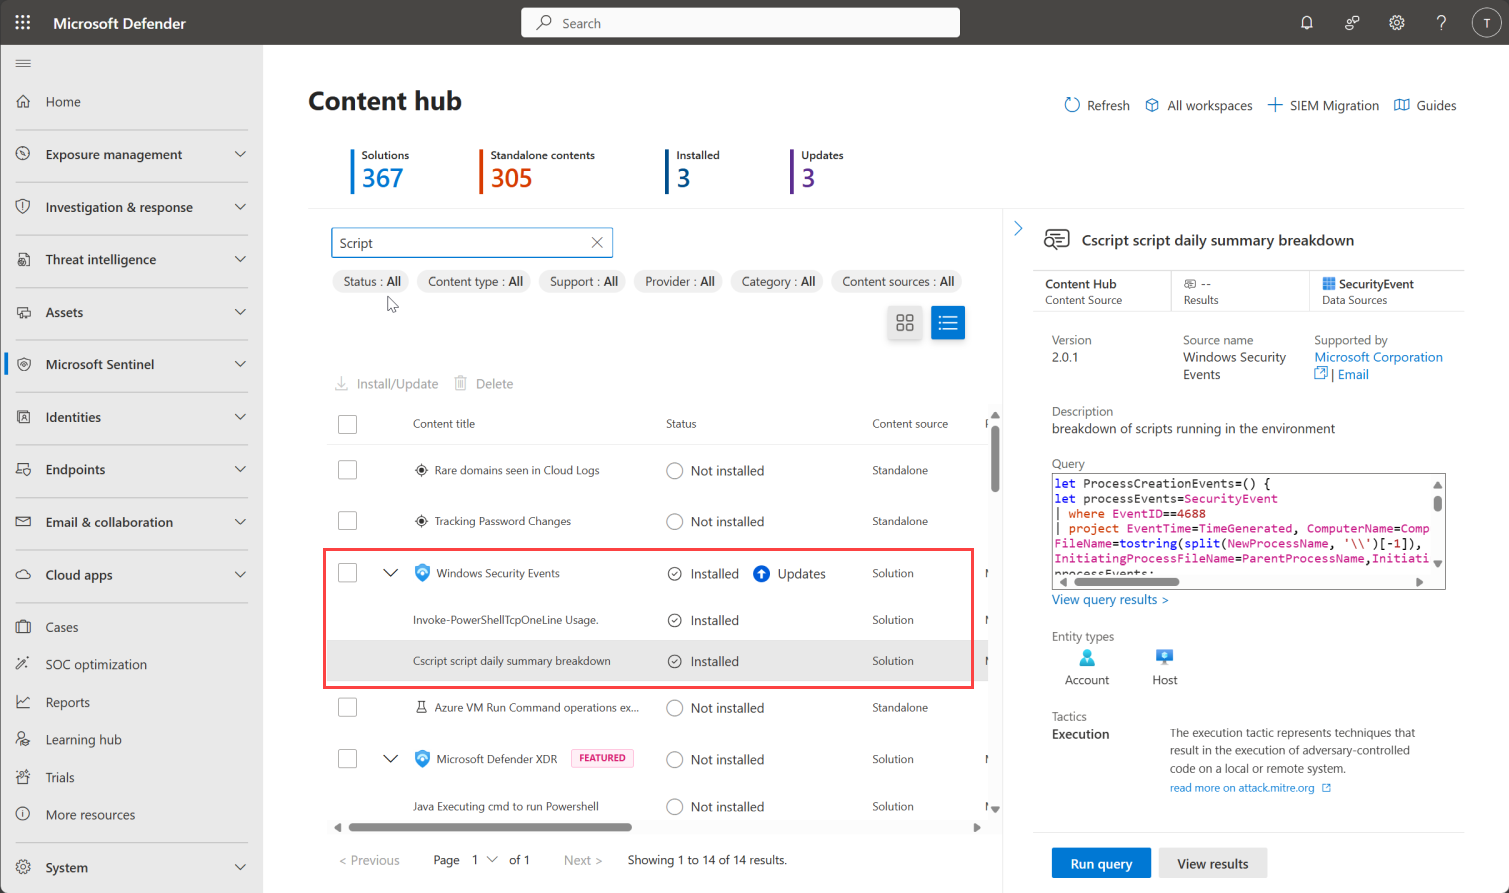 Use Content Hub templates with a production review Decide which response steps belong in a playbook
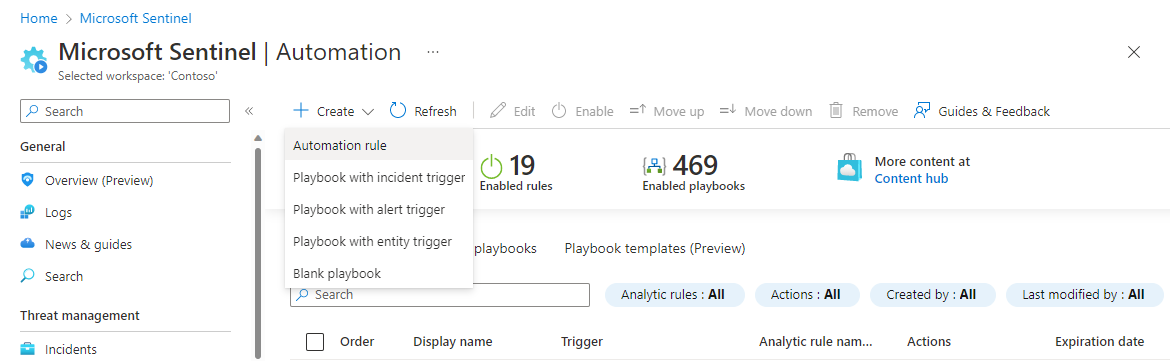 Build an automation rule with a clear owner Use a watchlist to enrich a detection query
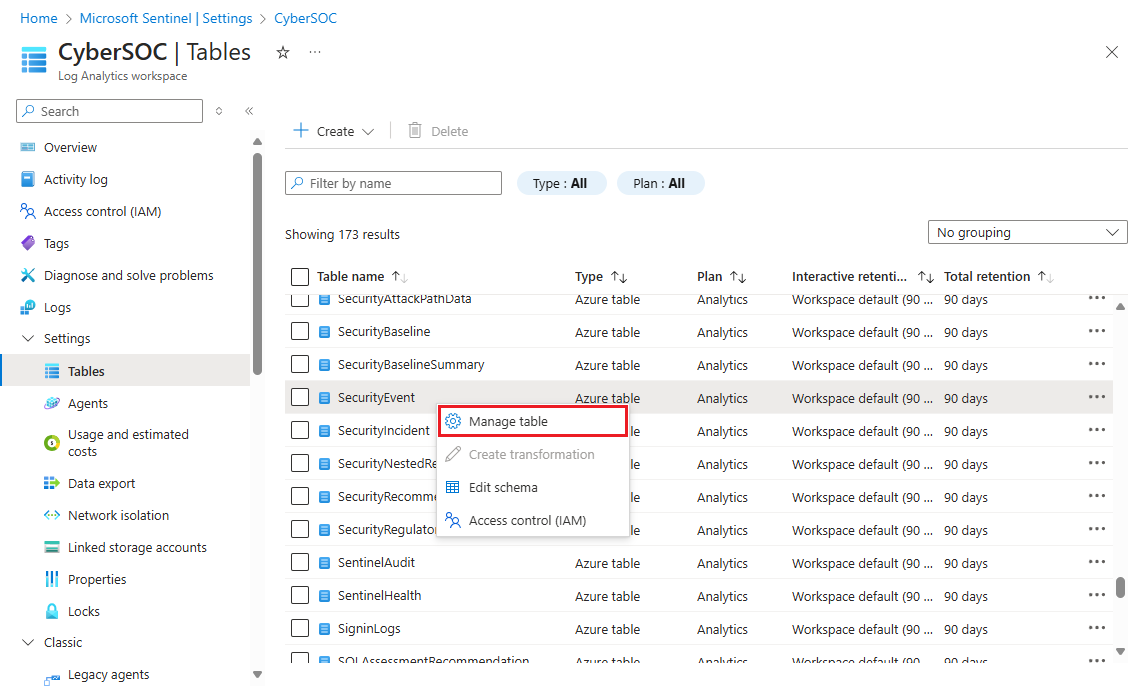 Choose retention settings around investigation needs
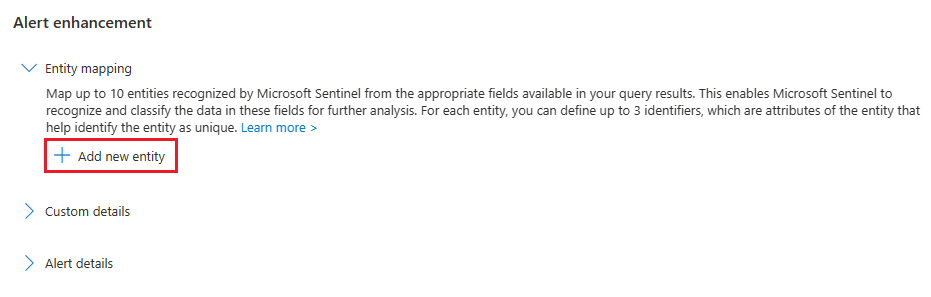 Map entities so incidents contain useful context Troubleshoot a Sentinel connector that stopped sending data
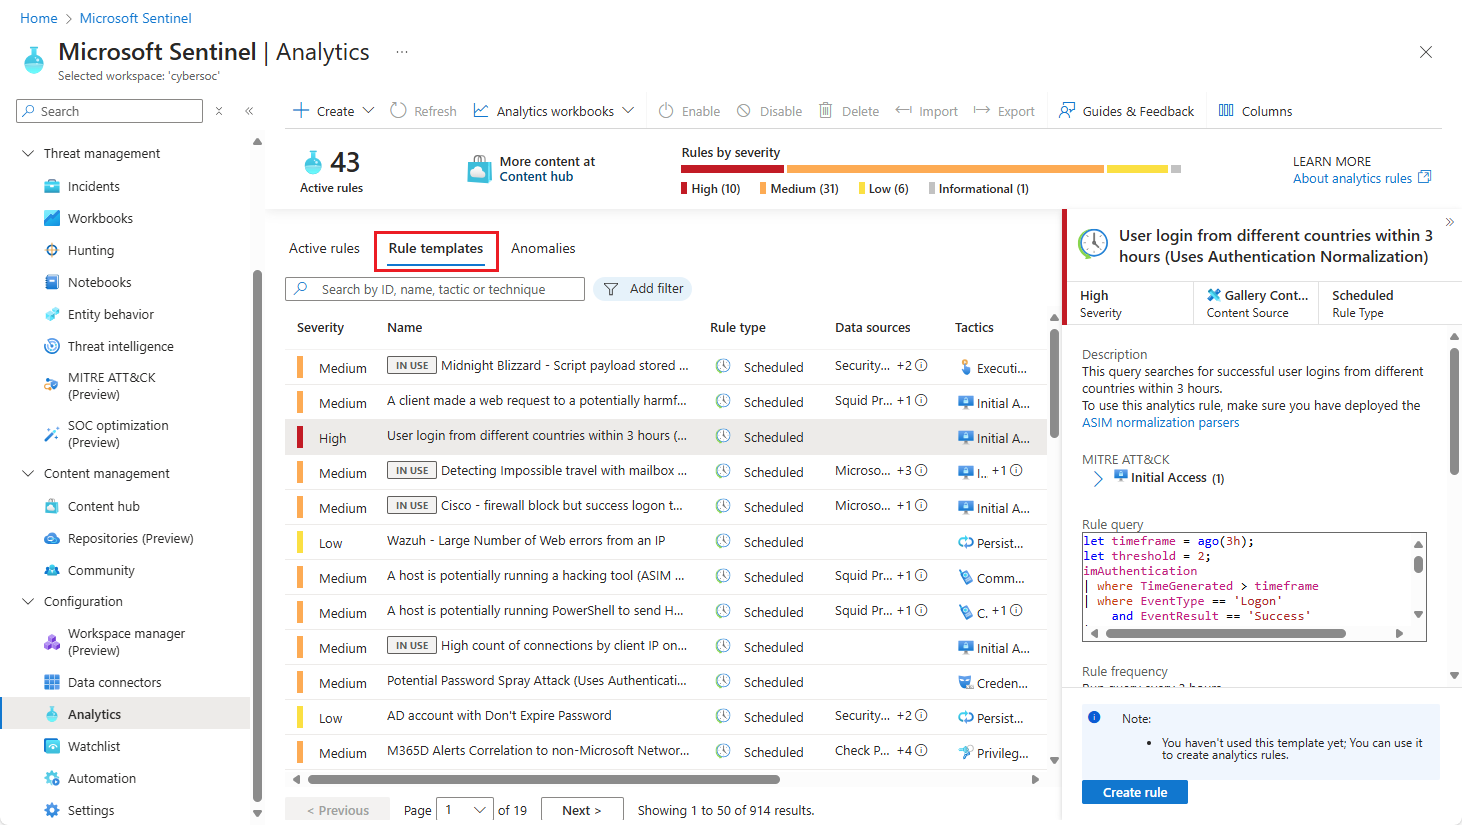 Turn a detection requirement into an analytics rule Create a useful KQL query for an initial investigation Connect Windows security events using Azure Monitor Agent
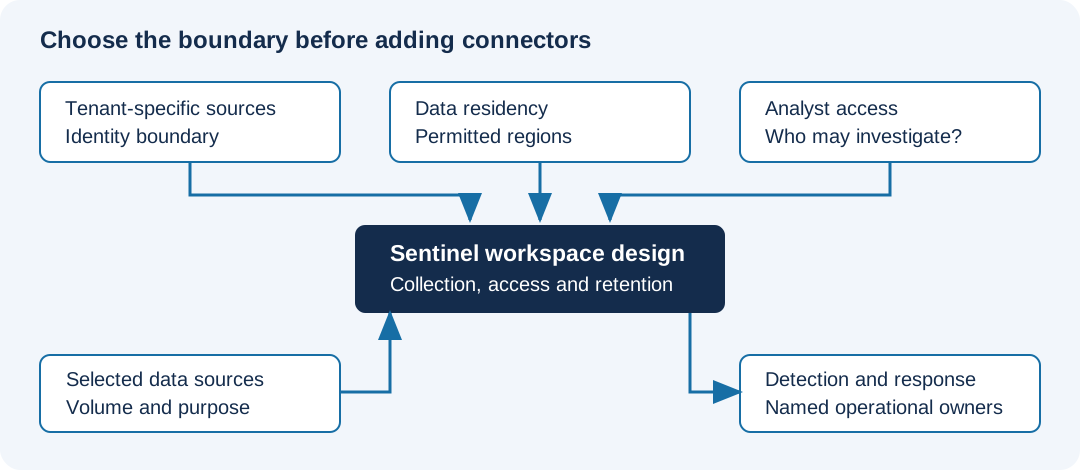 Plan a Sentinel workspace before connecting data
Choose a detection exclusion or a rule change Use Advanced Hunting to test a Defender XDR hypothesis Connect Sentinel incidents with Defender XDR context Investigate a rule that creates too many incidents Use Content Hub templates with a production review Decide which response steps belong in a playbook Build an automation rule with a clear owner Use a watchlist to enrich a detection query Choose retention settings around investigation needs Map entities so incidents contain useful context Troubleshoot a Sentinel connector that stopped sending data Turn a detection requirement into an analytics rule Create a useful KQL query for an initial investigation Connect Windows security events using Azure Monitor Agent Plan a Sentinel workspace before connecting data