
Identity & access
20 posts, newest first.
#access-reviews#administrative-units#authentication#authentication-strengths#automation#azure-administration#conditional-access#consent#cross-tenant-access#deployment-pipeline#emergency-access#external-users#github#github-actions#groups#guest-access#managed-identities#microsoft-entra-id#multifactor-authentication#openid-connect#permissions#powershell#privileged-access#privileged-identity-management#rbac#rbac-separation#sign-in-logs#troubleshooting#what-if-tool#workload-identities#workload-identity-federation
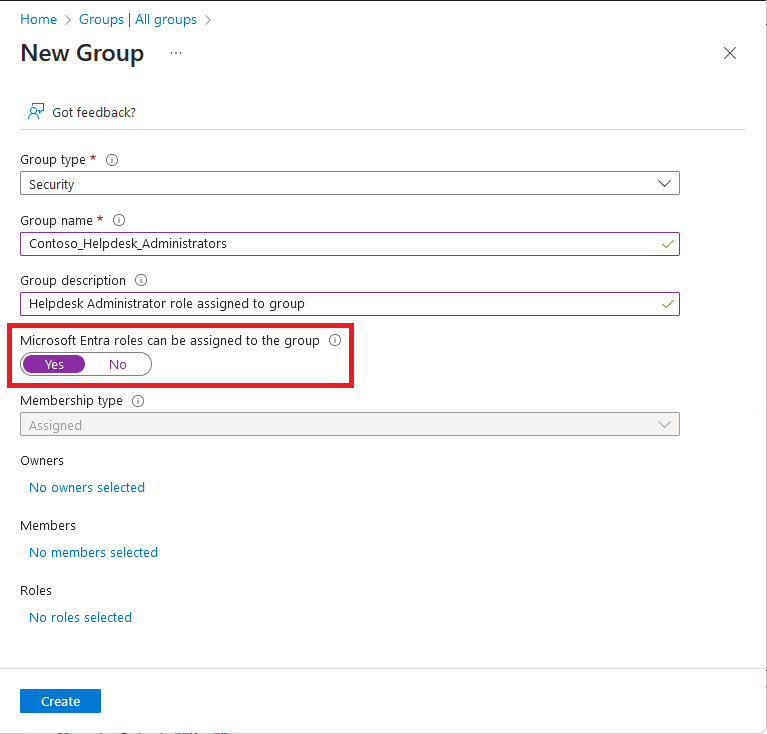 Build a repeatable privileged-access review Use role-assignable groups and PIM to manage privileged access reviews, ensuring clear separation between group membership and role eligibility.
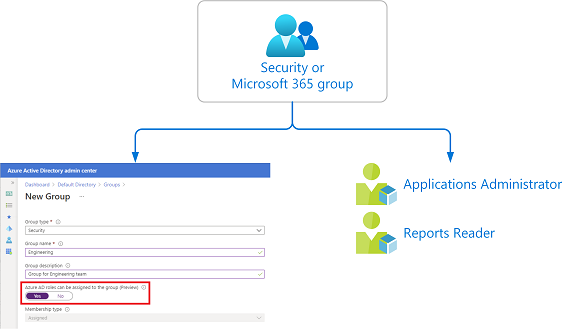 Use group-based administration without hiding excessive access
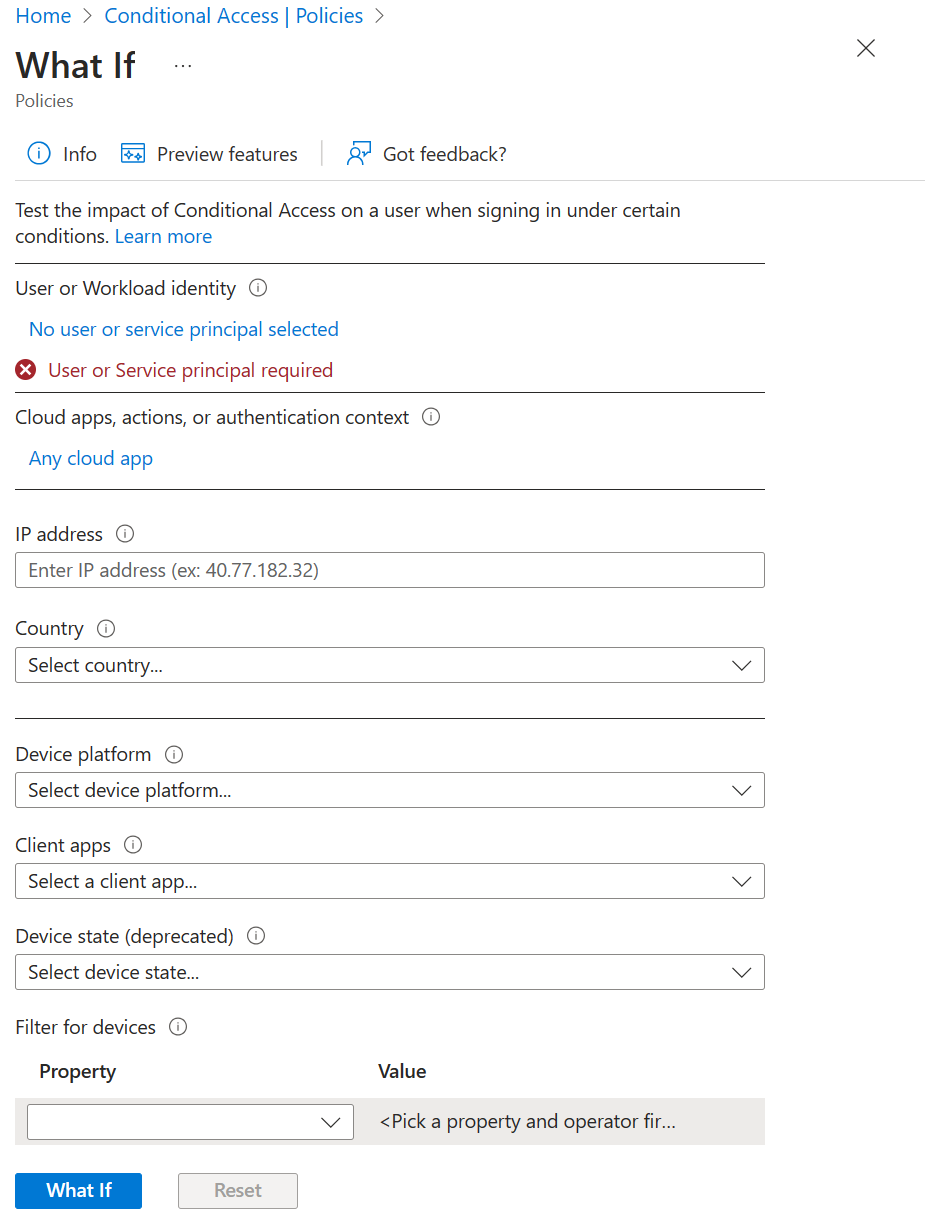 Investigate an unexpected Conditional Access result
All posts in this category
Review application consent and service principal permissions Plan identity permissions for a production deployment pipeline Use Conditional Access authentication strengths carefully 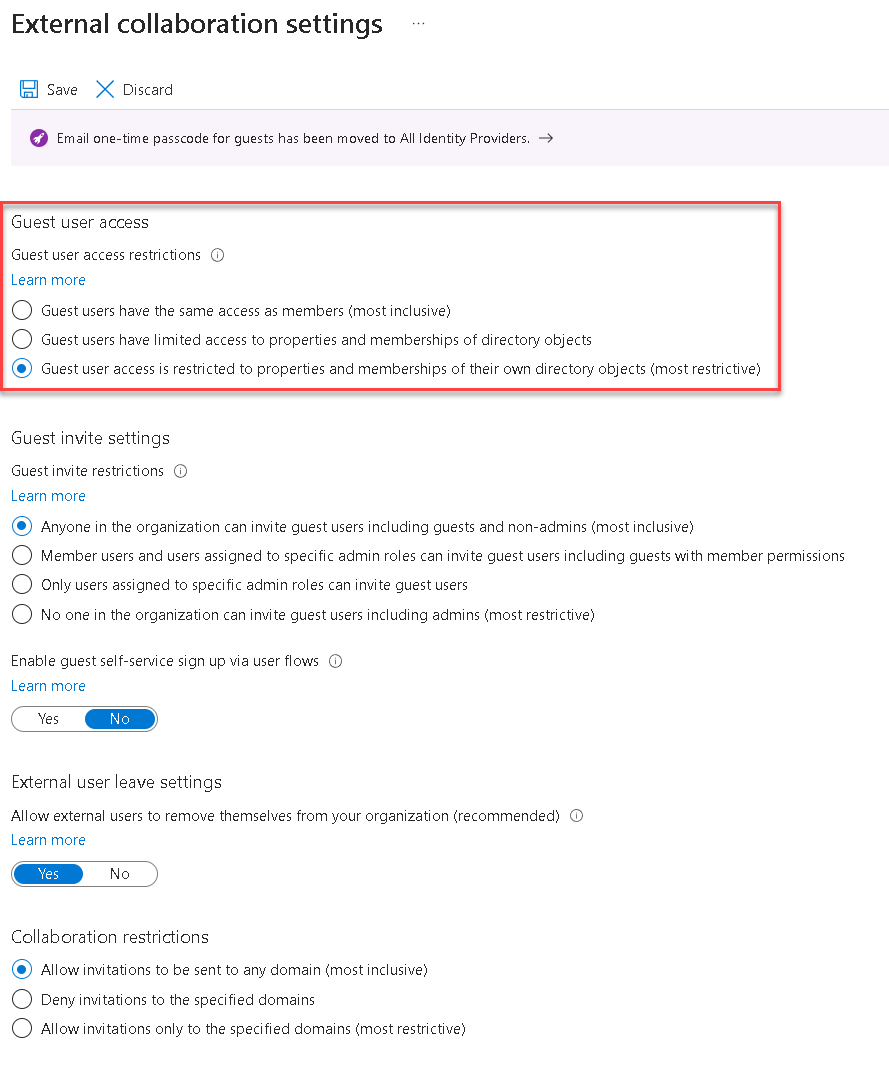 Review guest access before sharing an Azure application Troubleshoot a managed identity that cannot reach a resource
 Require stronger authentication for privileged operations Decide where Azure RBAC assignments should live
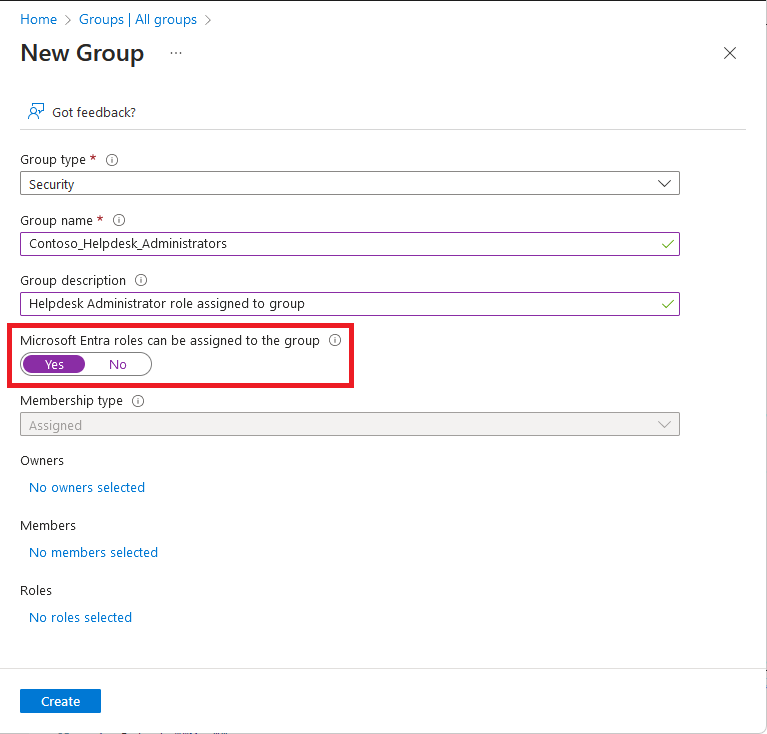 Run an access review for privileged group membership Separate Azure control-plane roles from data-plane permissions
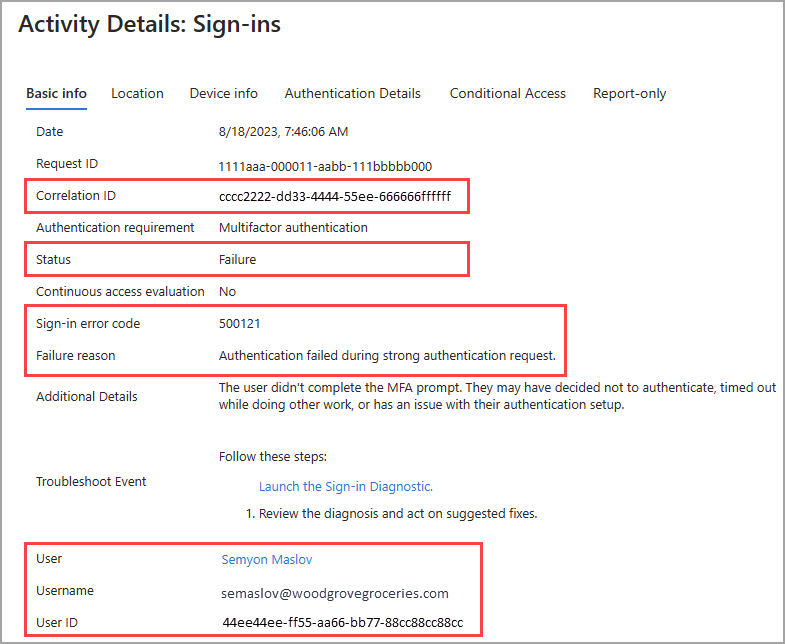 Investigate a failed sign-in using Entra logs Connect GitHub Actions to Azure using OpenID Connect Prepare Azure administrators for mandatory multifactor authentication Replace a service principal secret with workload identity federation
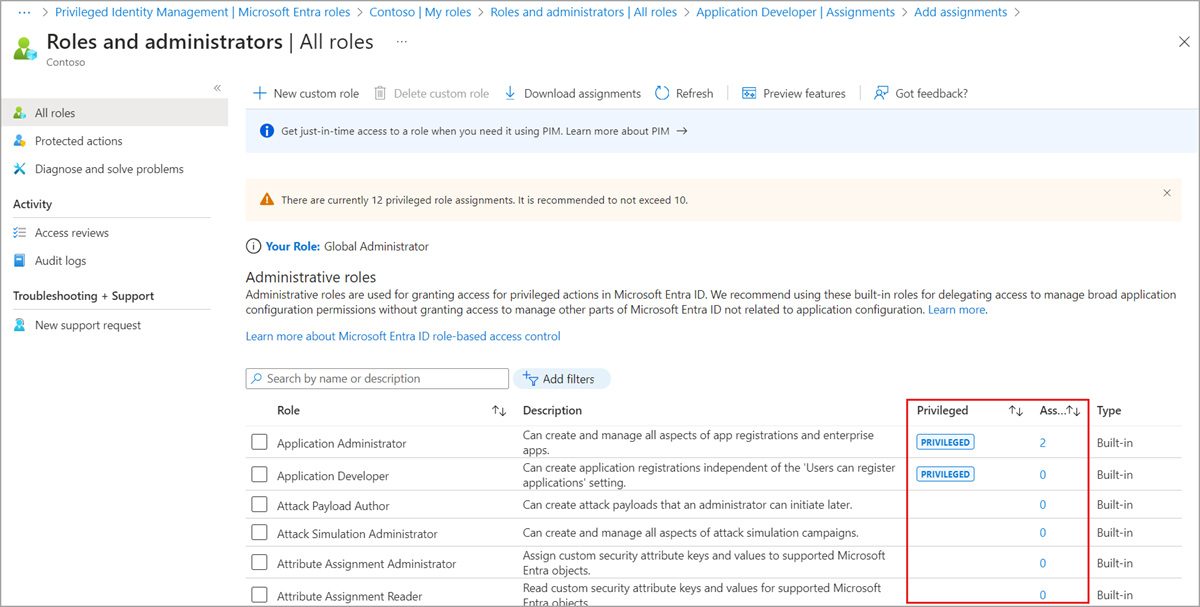 Use Privileged Identity Management for Azure administration Choose system-assigned or user-assigned managed identities
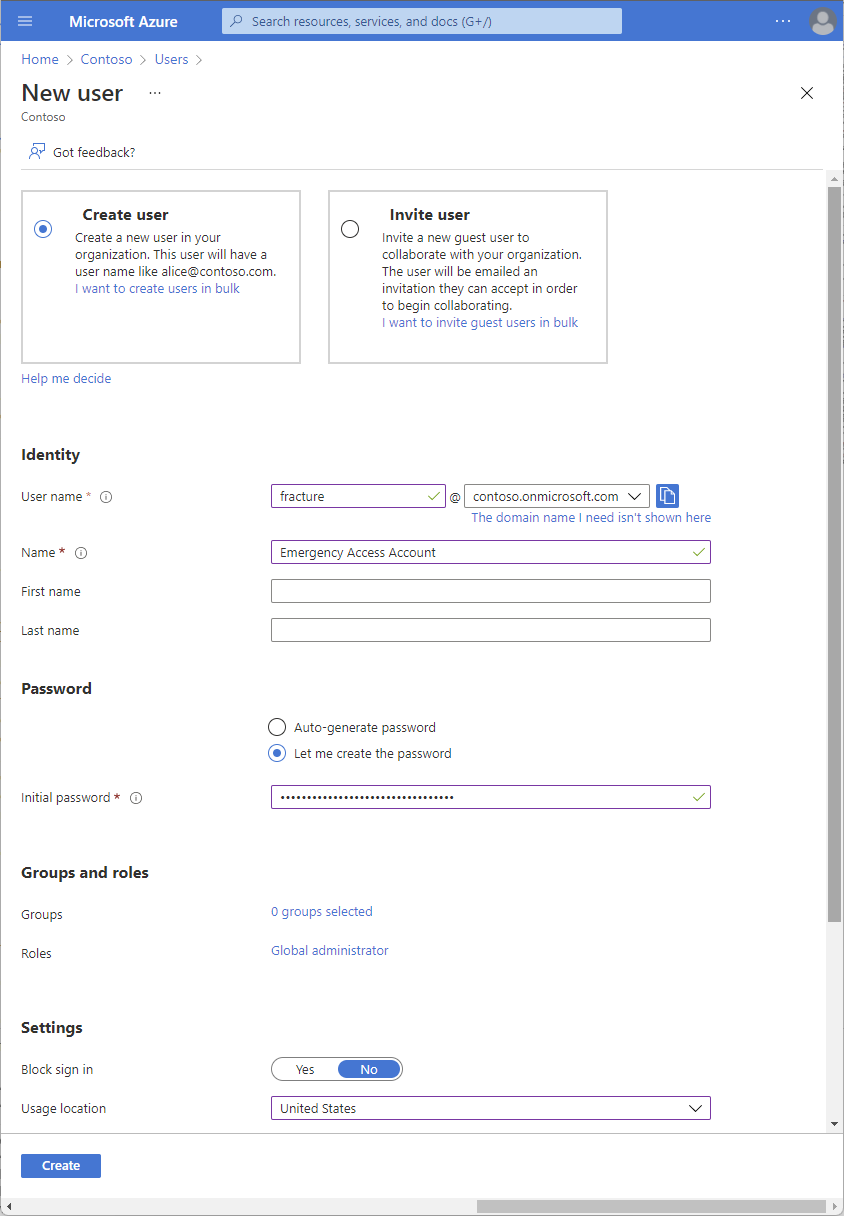 Create and test emergency access accounts in Microsoft Entra ID
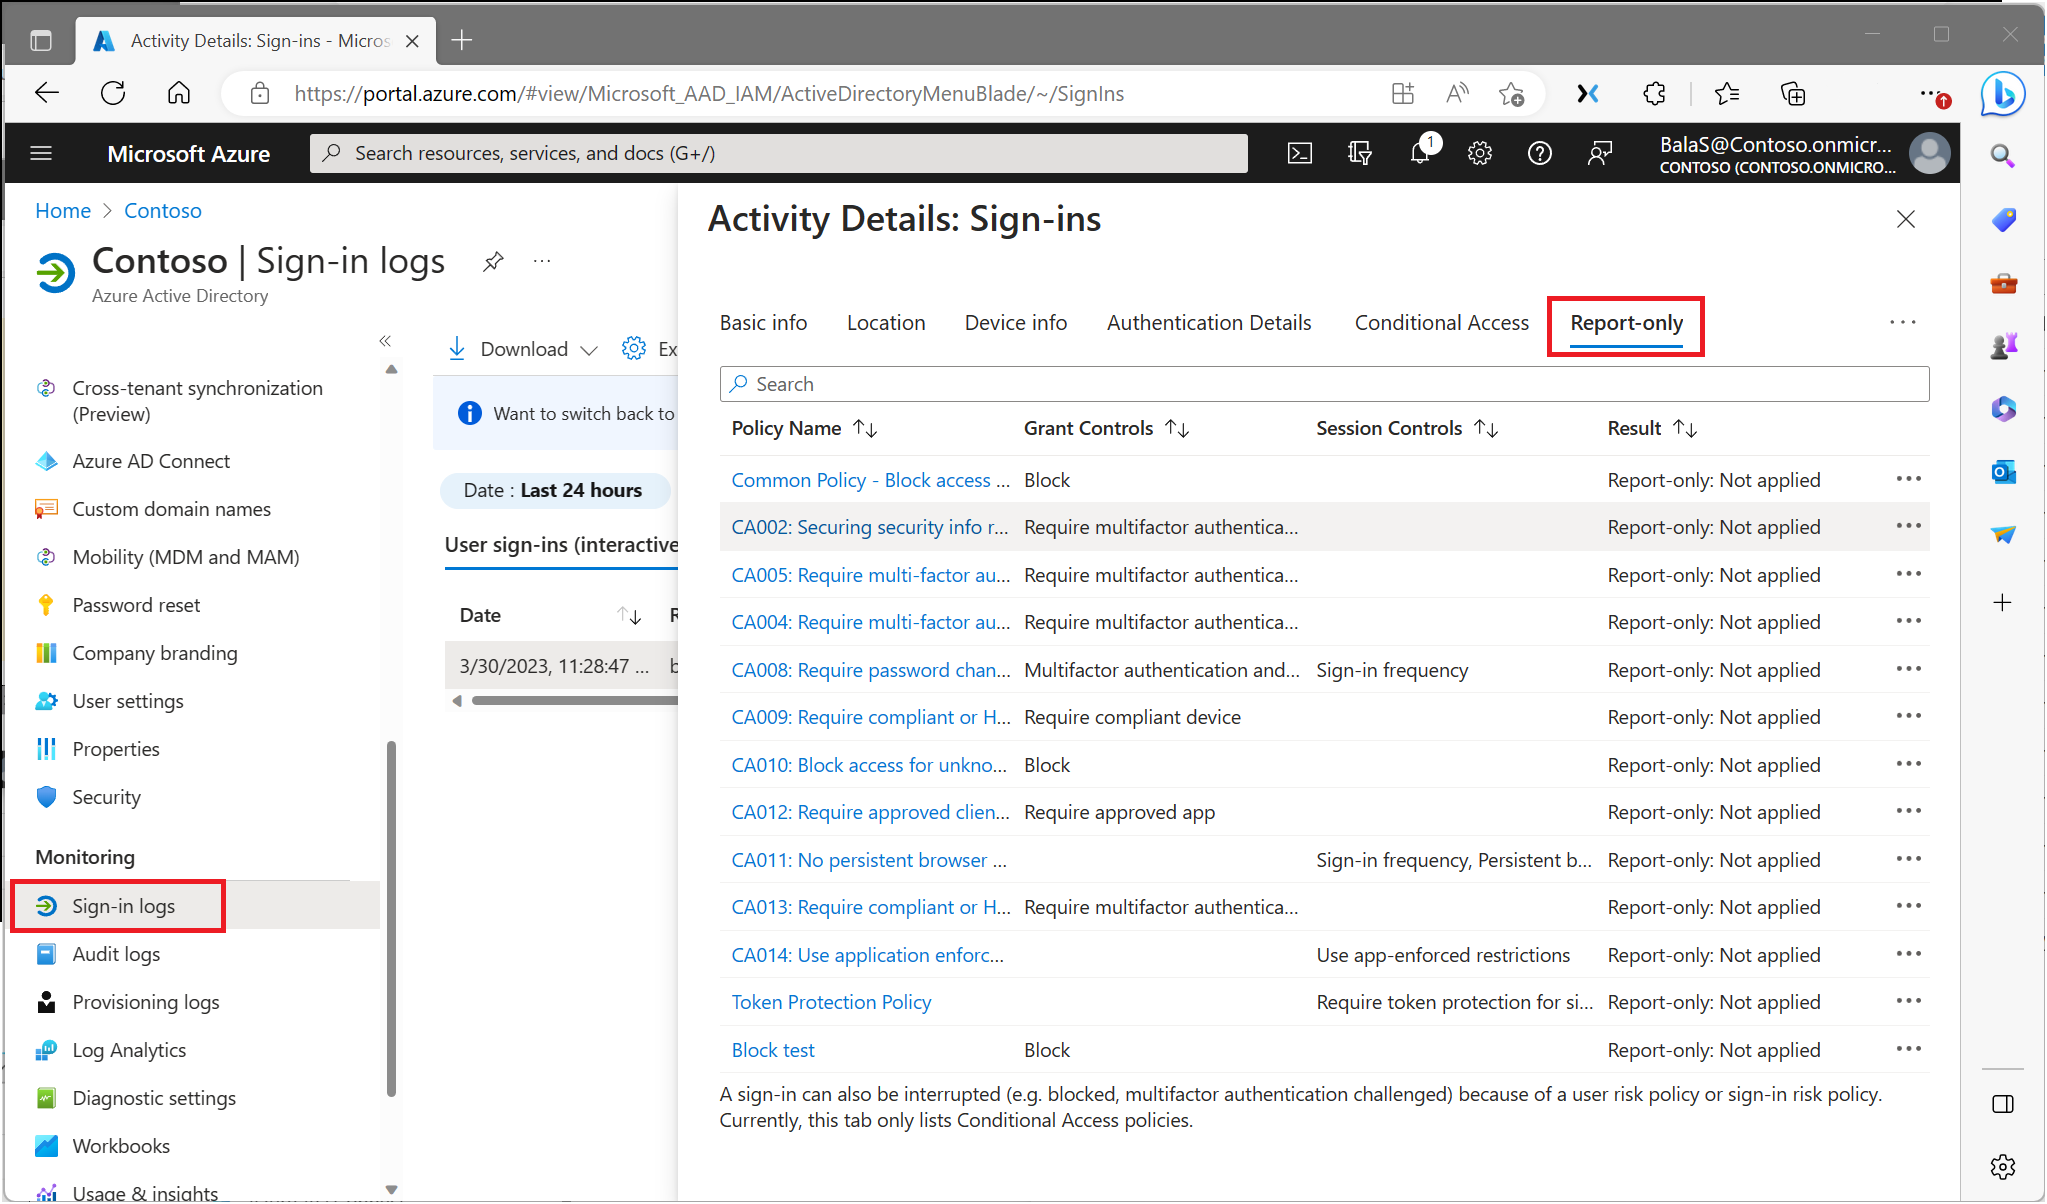 Roll out Conditional Access using report-only mode
 Review guest access before sharing an Azure application Troubleshoot a managed identity that cannot reach a resource Require stronger authentication for privileged operations Decide where Azure RBAC assignments should live Run an access review for privileged group membership Separate Azure control-plane roles from data-plane permissions Investigate a failed sign-in using Entra logs Connect GitHub Actions to Azure using OpenID Connect Prepare Azure administrators for mandatory multifactor authentication Replace a service principal secret with workload identity federation Use Privileged Identity Management for Azure administration Choose system-assigned or user-assigned managed identities Create and test emergency access accounts in Microsoft Entra ID Roll out Conditional Access using report-only mode