
#log-analytics
10 artigos, mais recentes primeiro.
Plan access separation between security operations teams  Apply diagnostic settings consistently across Azure resources Review log ingestion cost alongside retention requirements
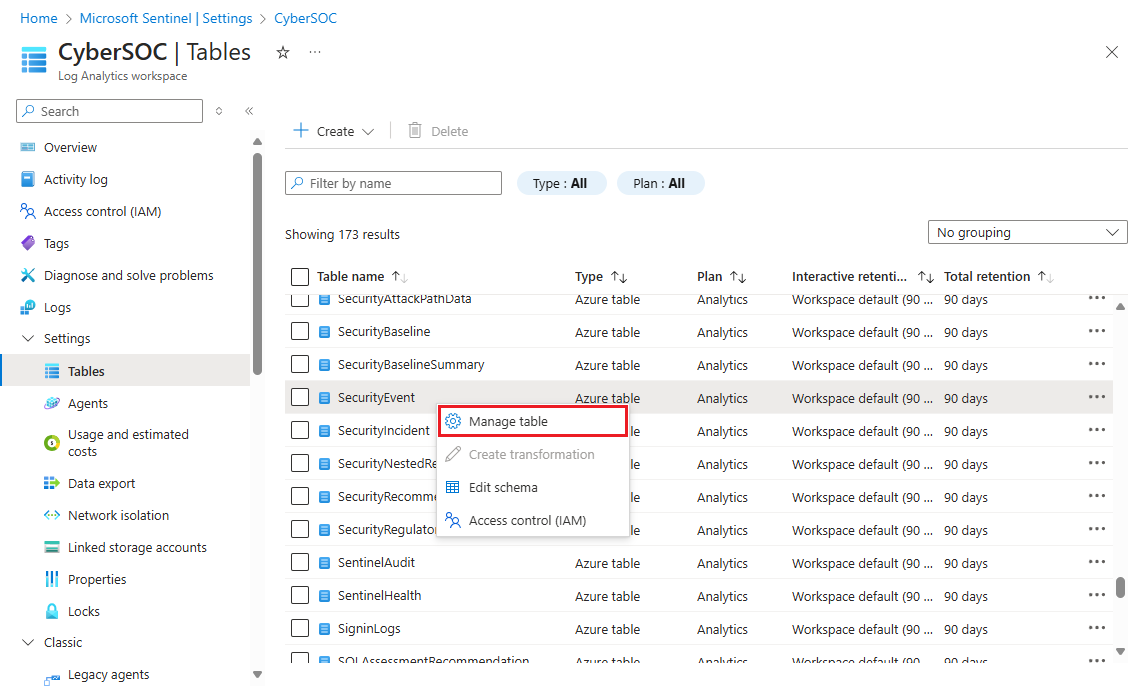 Choose retention settings around investigation needs
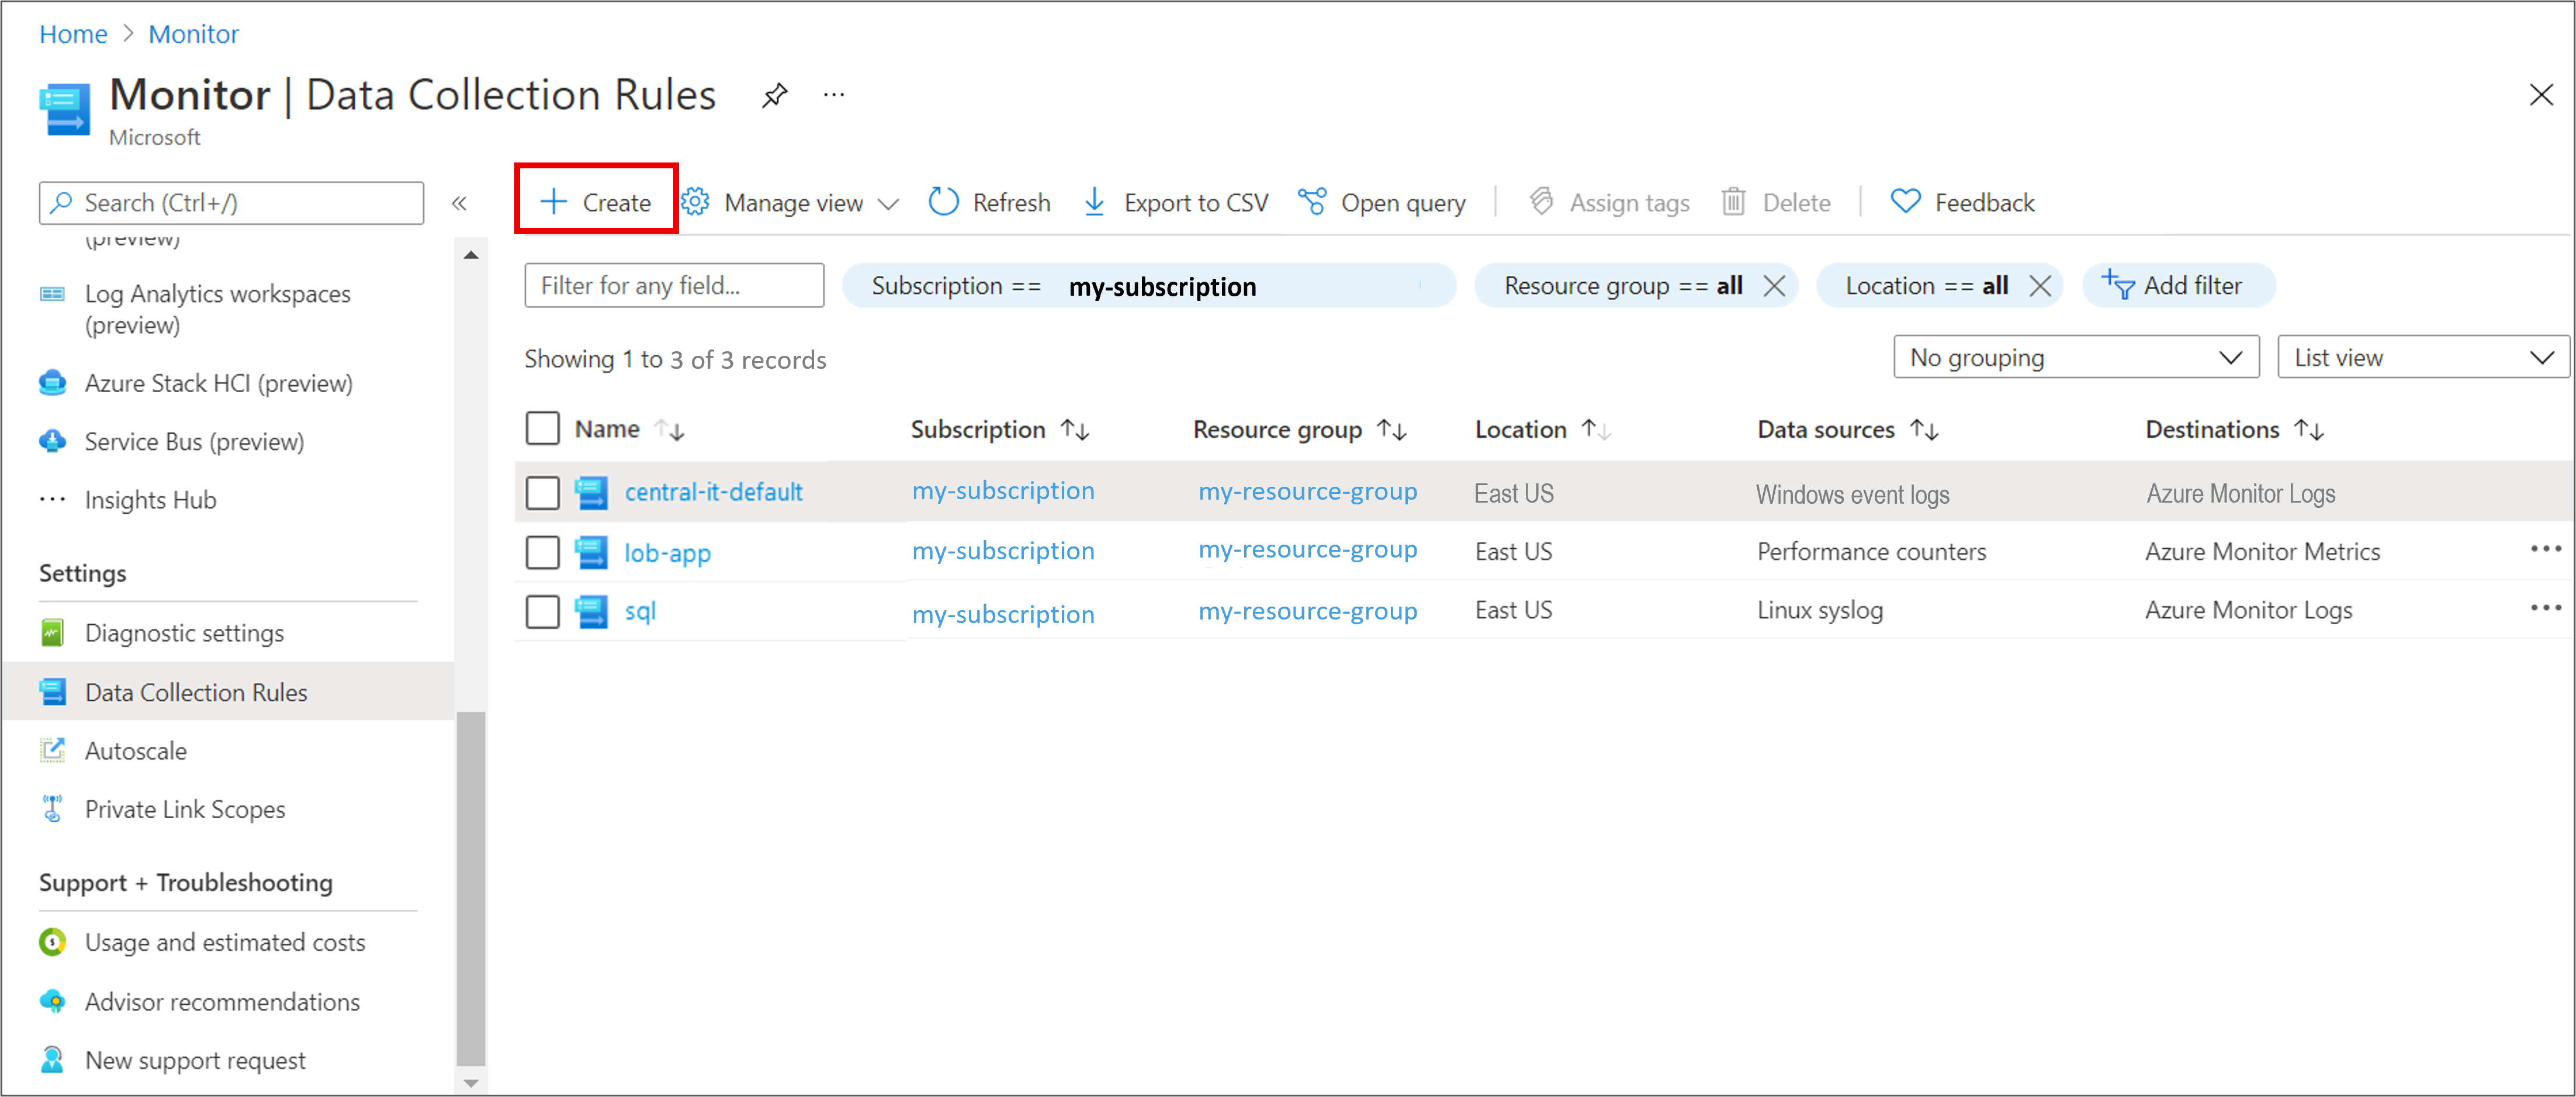 Use data collection rules to control server telemetry Choose a Log Analytics workspace boundary Compare Defender plan coverage across subscriptions
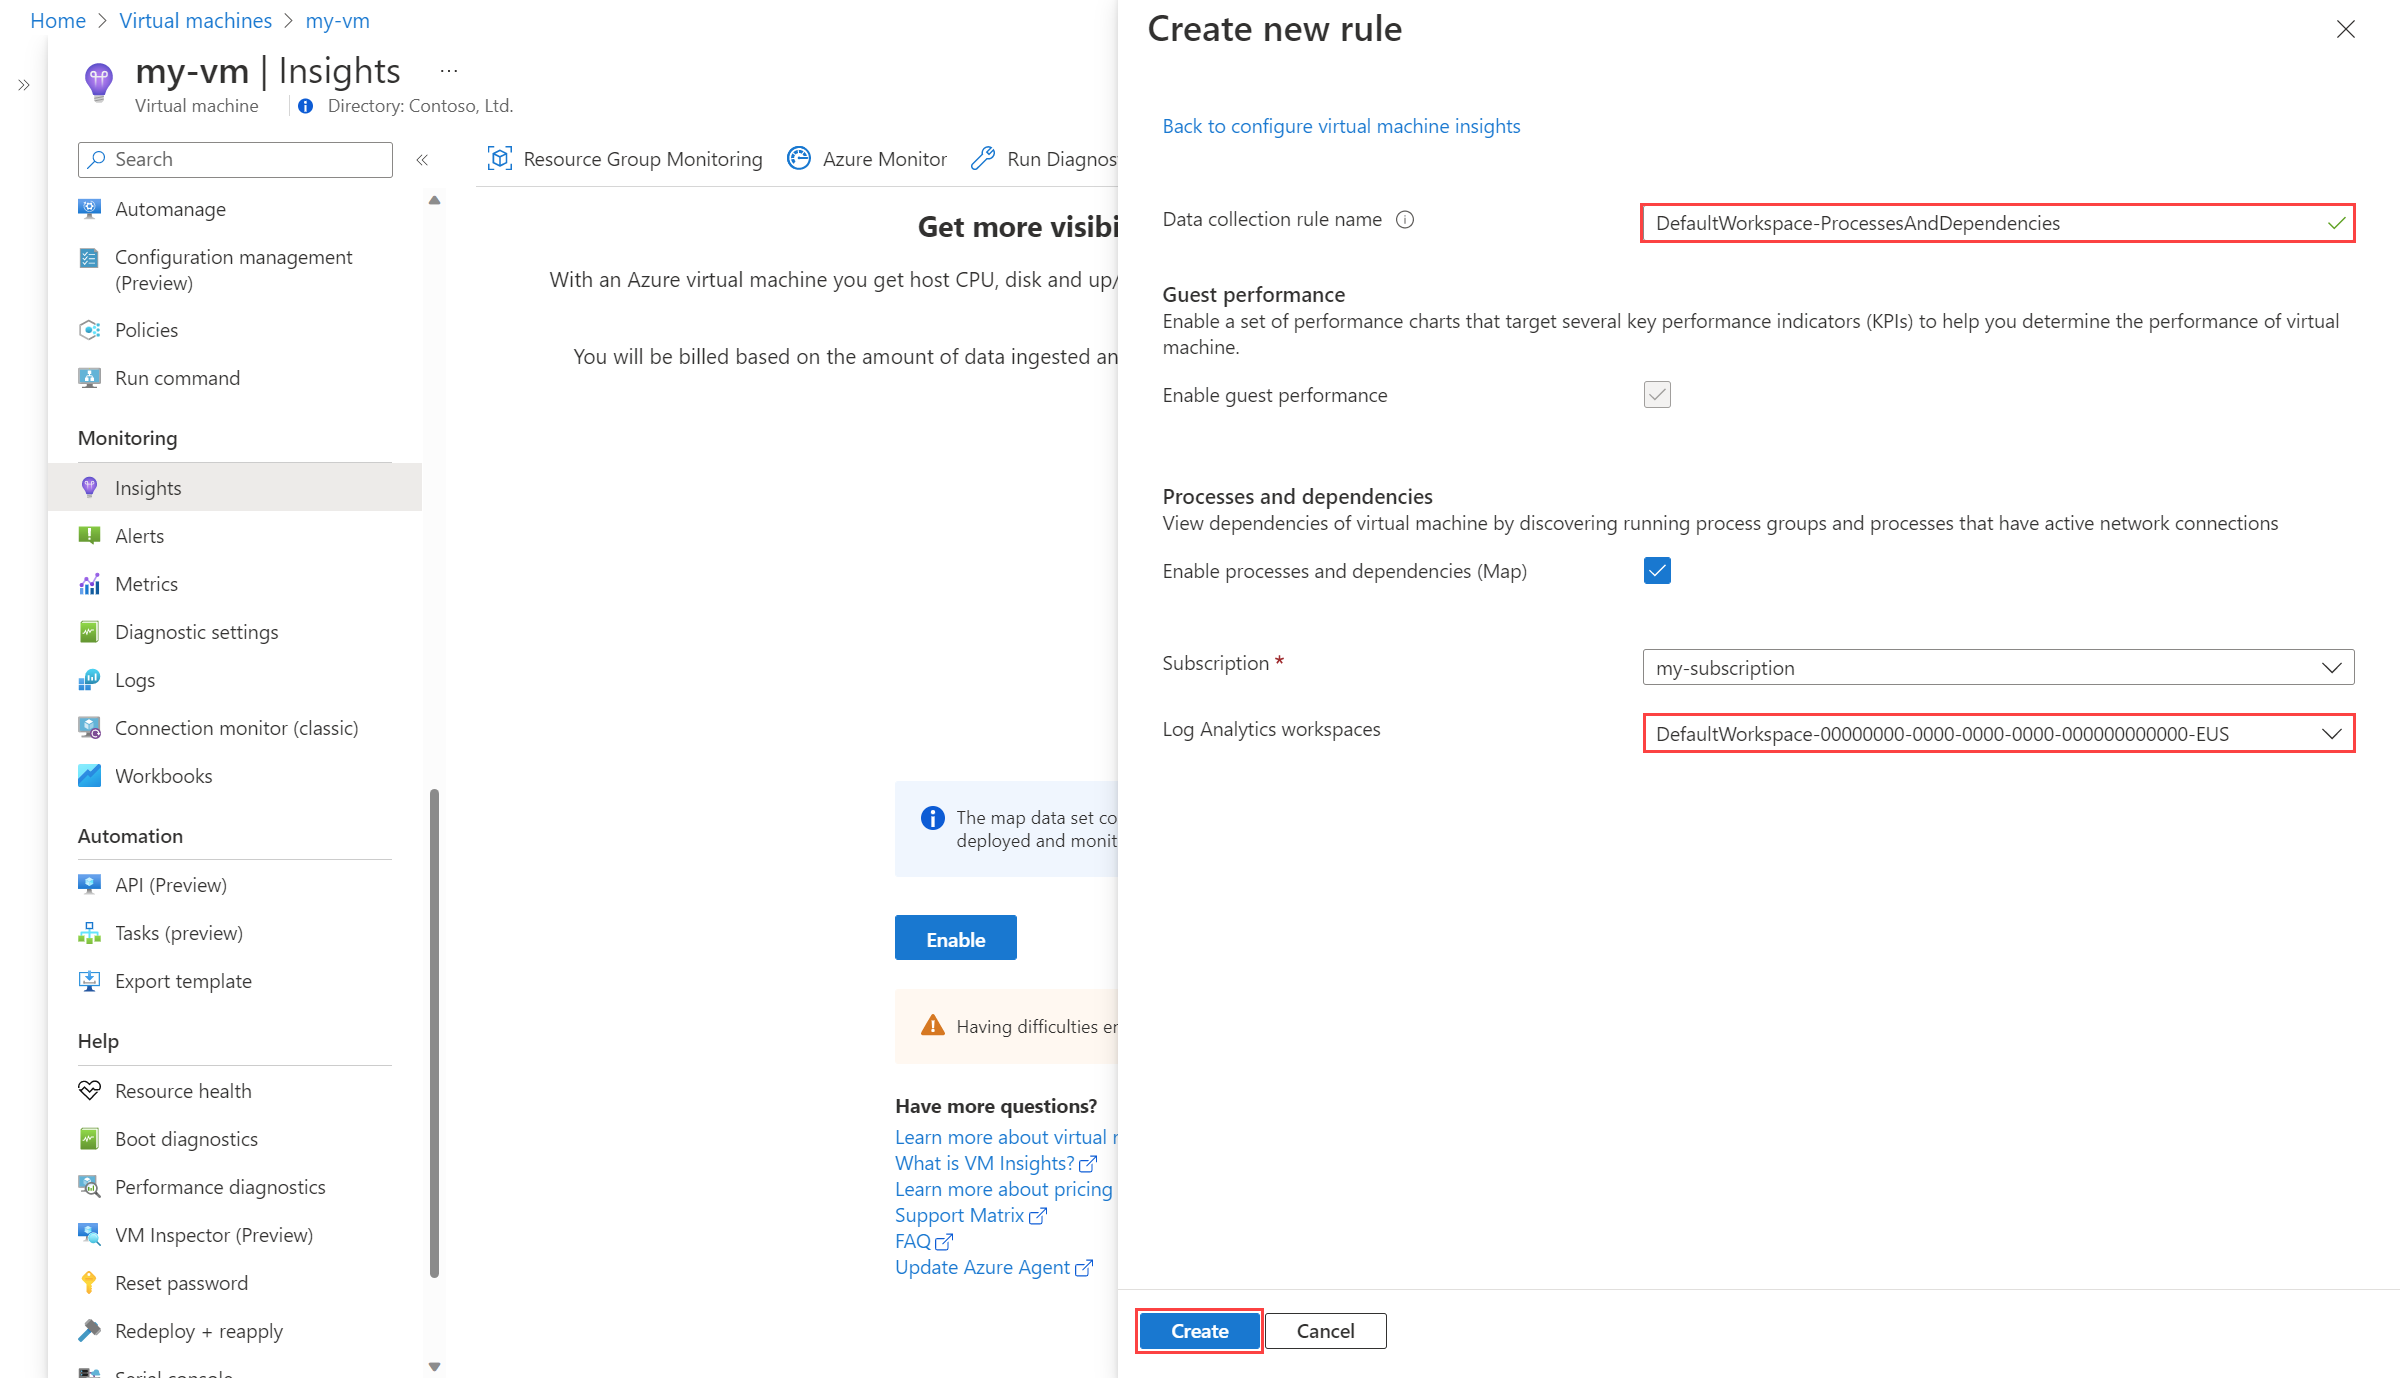 Configure VM insights for a group of Azure servers
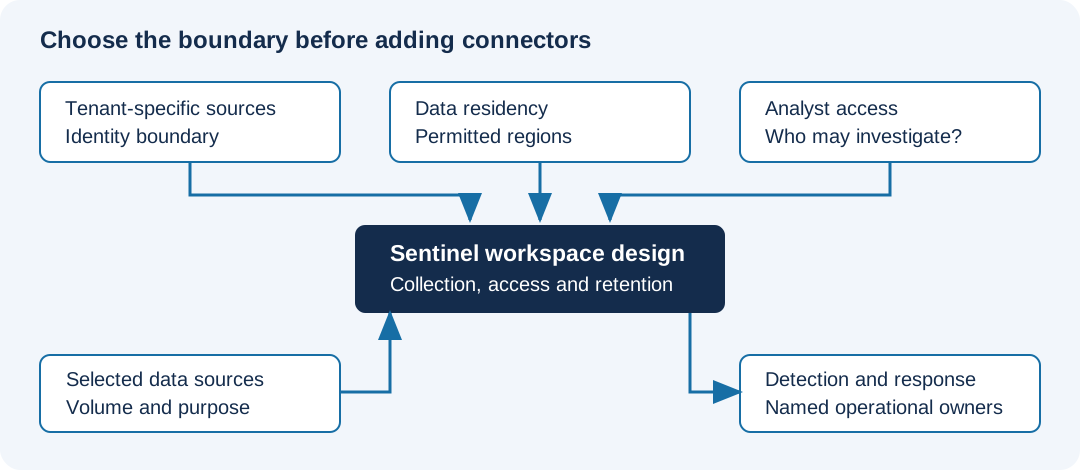 Plan a Sentinel workspace before connecting data
 Multiple Azure Subscriptions with one OMS Workspace
 Apply diagnostic settings consistently across Azure resources Review log ingestion cost alongside retention requirements Choose retention settings around investigation needs Use data collection rules to control server telemetry Choose a Log Analytics workspace boundary Compare Defender plan coverage across subscriptions Configure VM insights for a group of Azure servers Plan a Sentinel workspace before connecting data Multiple Azure Subscriptions with one OMS Workspace