
#kql
11 artigos, mais recentes primeiro.
Review connector health and ingestion changes together Design a dashboard with clear service ownership Build an incident triage workbook for the operations team 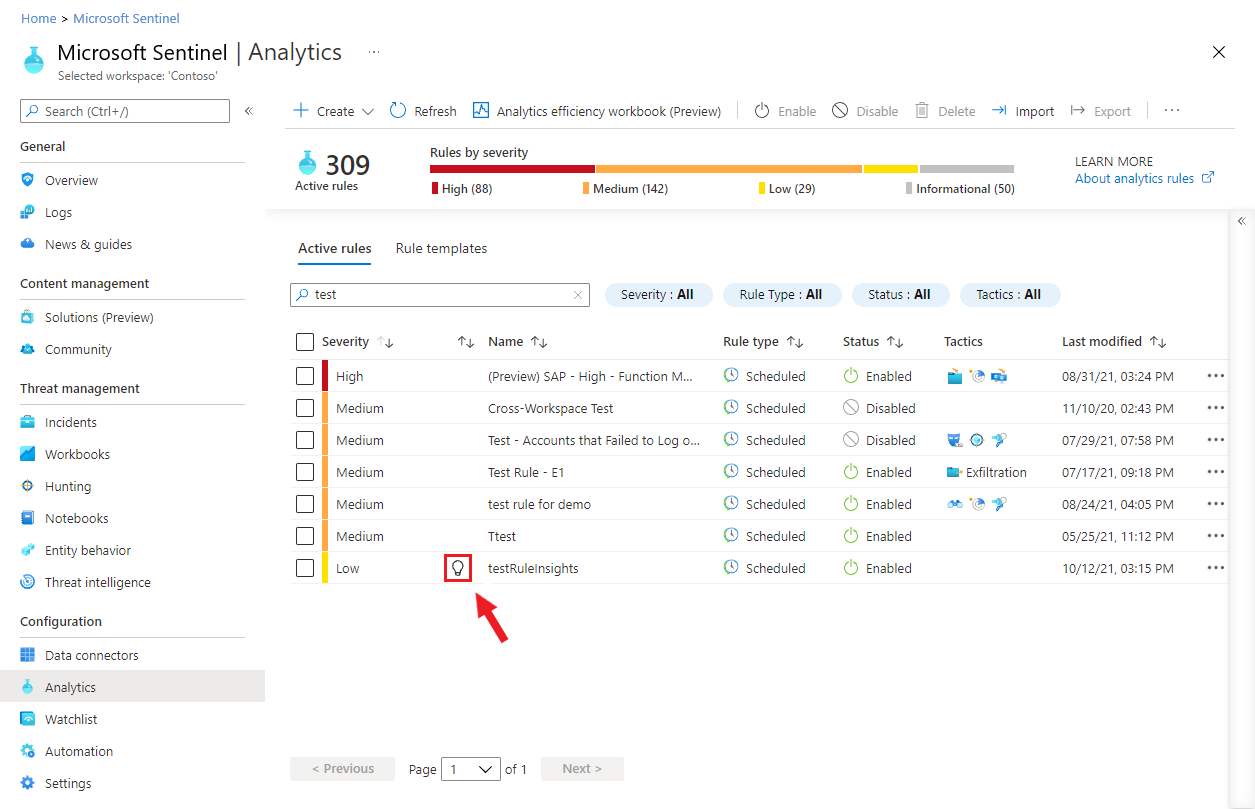 Choose a detection exclusion or a rule change
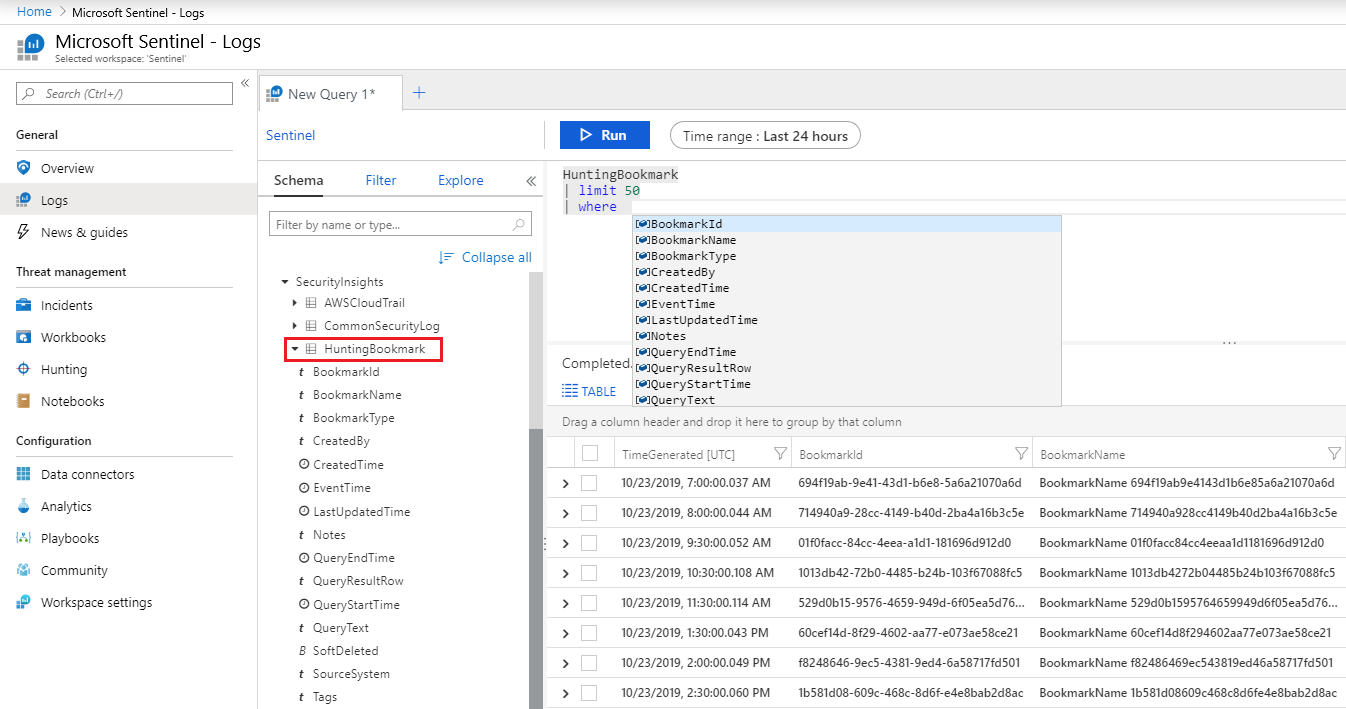 Use Advanced Hunting to test a Defender XDR hypothesis Connect Sentinel incidents with Defender XDR context Use a watchlist to enrich a detection query
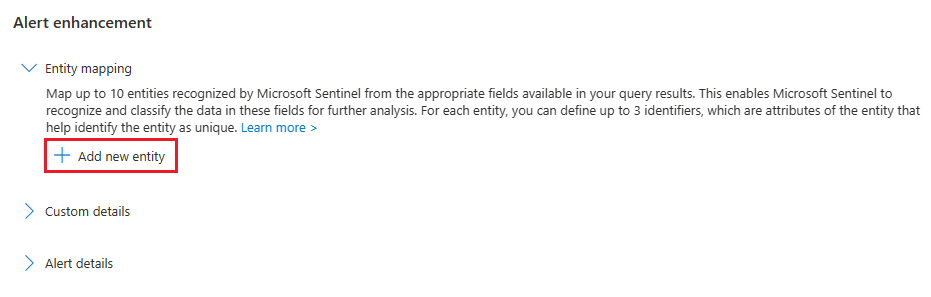 Map entities so incidents contain useful context
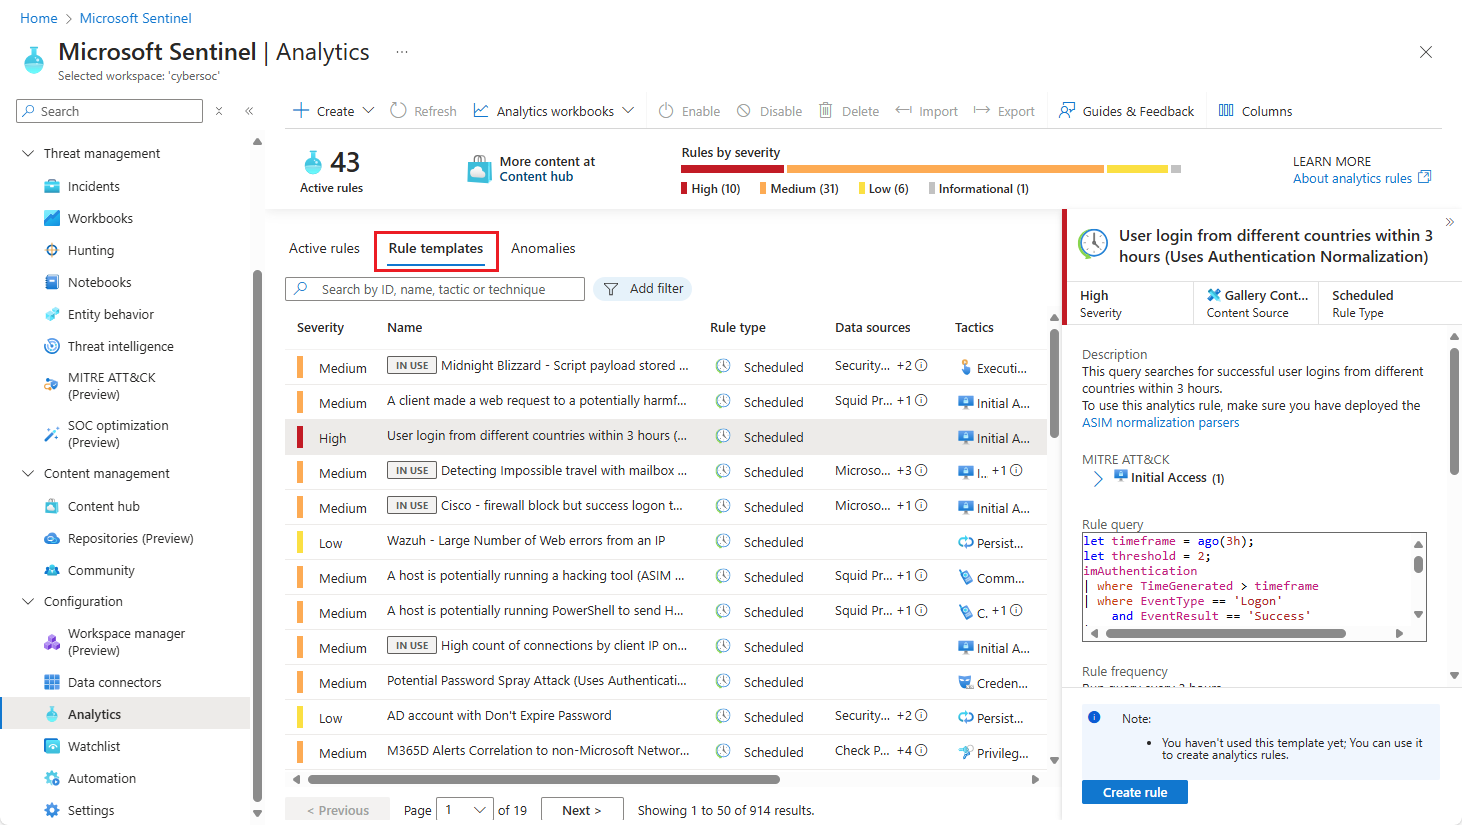 Turn a detection requirement into an analytics rule Create a useful KQL query for an initial investigation What Copilot for Security can help a security team investigate
 Choose a detection exclusion or a rule change Use Advanced Hunting to test a Defender XDR hypothesis Connect Sentinel incidents with Defender XDR context Use a watchlist to enrich a detection query Map entities so incidents contain useful context Turn a detection requirement into an analytics rule Create a useful KQL query for an initial investigation What Copilot for Security can help a security team investigate